AI finds Java flaw in 1 hour with Codex
Security firm Calif said on the 17th of November 2026 that it used AI to find a serious flaw in Java. Java is software that runs many big business apps.
 AI helps find a big Java flaw
Security firm Calif said on the 17th of November 2026 that it used AI to find a serious flaw in Java. Java is software that runs many big business apps.
The flaw, called Java4Shell, can let attackers run their own code on some systems, BleepingComputer reported. Oracle released a fix the same day.
How AI found it
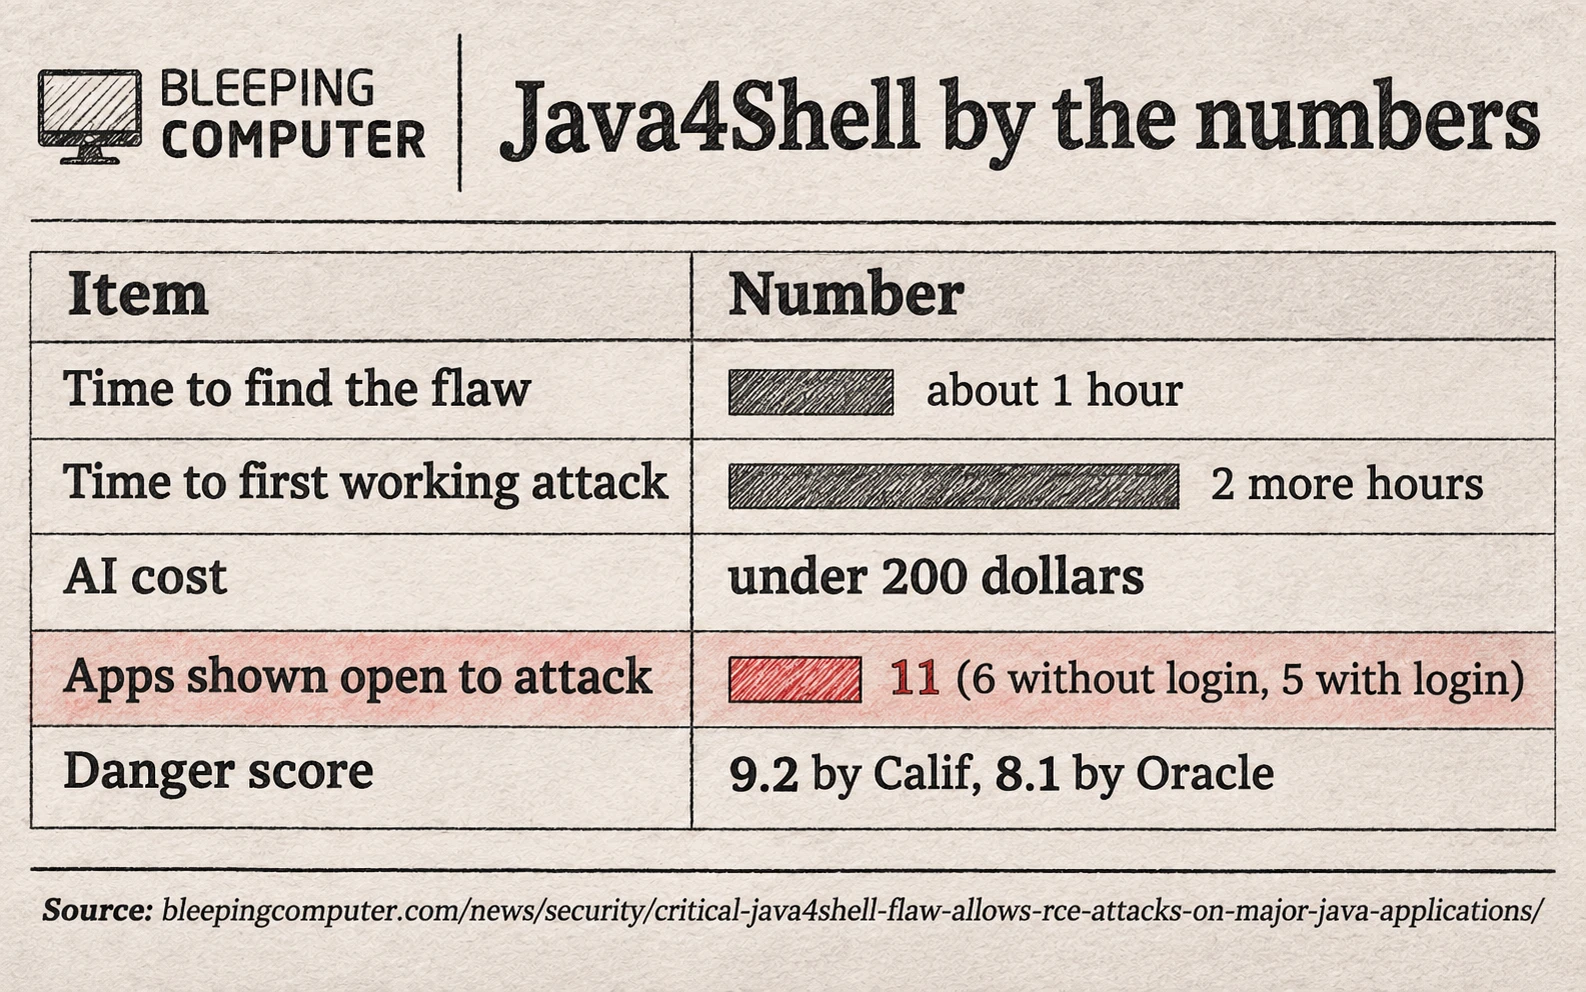
Calif researcher Quang Luong found the flaw with Codex, OpenAI's coding agent, BleepingComputer reported. He found it in about an hour.
He built a first working attack in two more hours, Calif said. The AI cost was under 200 dollars.
Who is at risk
The bug sits in a part of Java that decodes Base64, a common way to pack data as text. It only hits some Intel and AMD style chips with a feature called AVX-512.
Calif ran attacks on apps like Jenkins, Jira, Confluence and Keycloak in their default setup, BleepingComputer said. The US cyber agency CISA told users to patch right away.
Below we break down the numbers
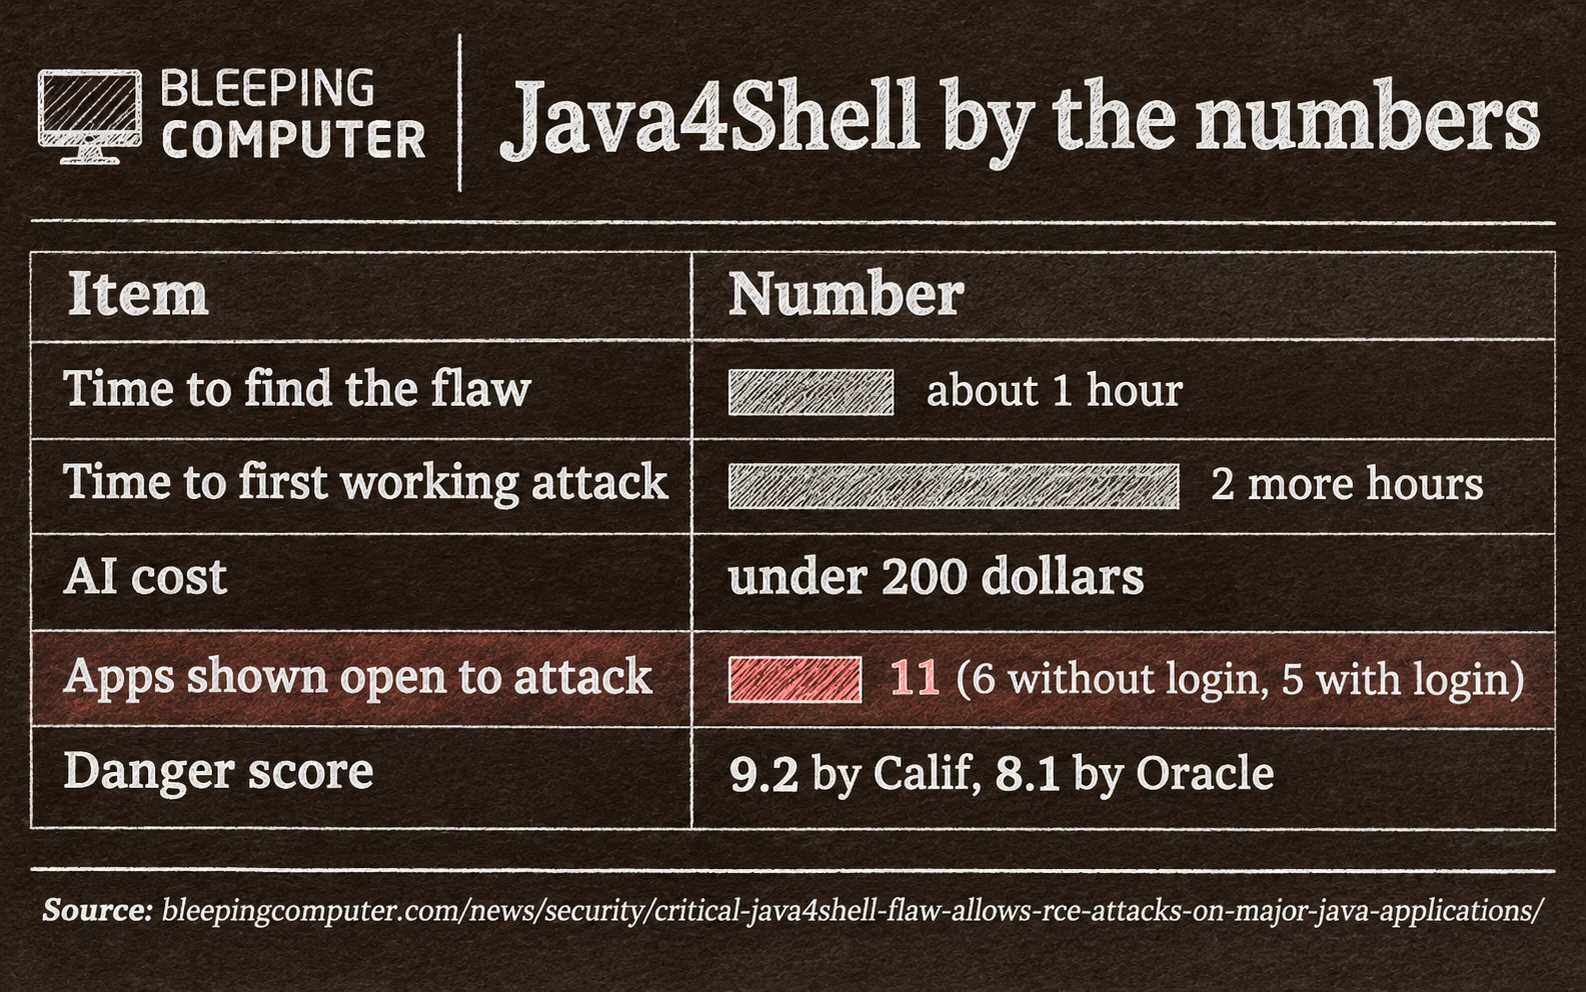
Calif rated the flaw 9.2 out of 10 for danger. Oracle rated it 8.1, a lower score on an older scale.
Finding and building the attack took about three hours in total. Calif listed six apps open to attack without a login and five more with a login, so eleven apps, by our count.
What is confirmed and what is not
Calif has not released its full attacks, only a simple test. There are no public reports yet of attacks in the wild.
Key facts
Calif disclosed Java4Shell on the 17th of November 2026.
A researcher found it with OpenAI's Codex in about an hour.
The AI cost was under 200 dollars.
Oracle released a fix on the 17th of November 2026.