Arista VeloCloud zero-day rated 9.9 exploited
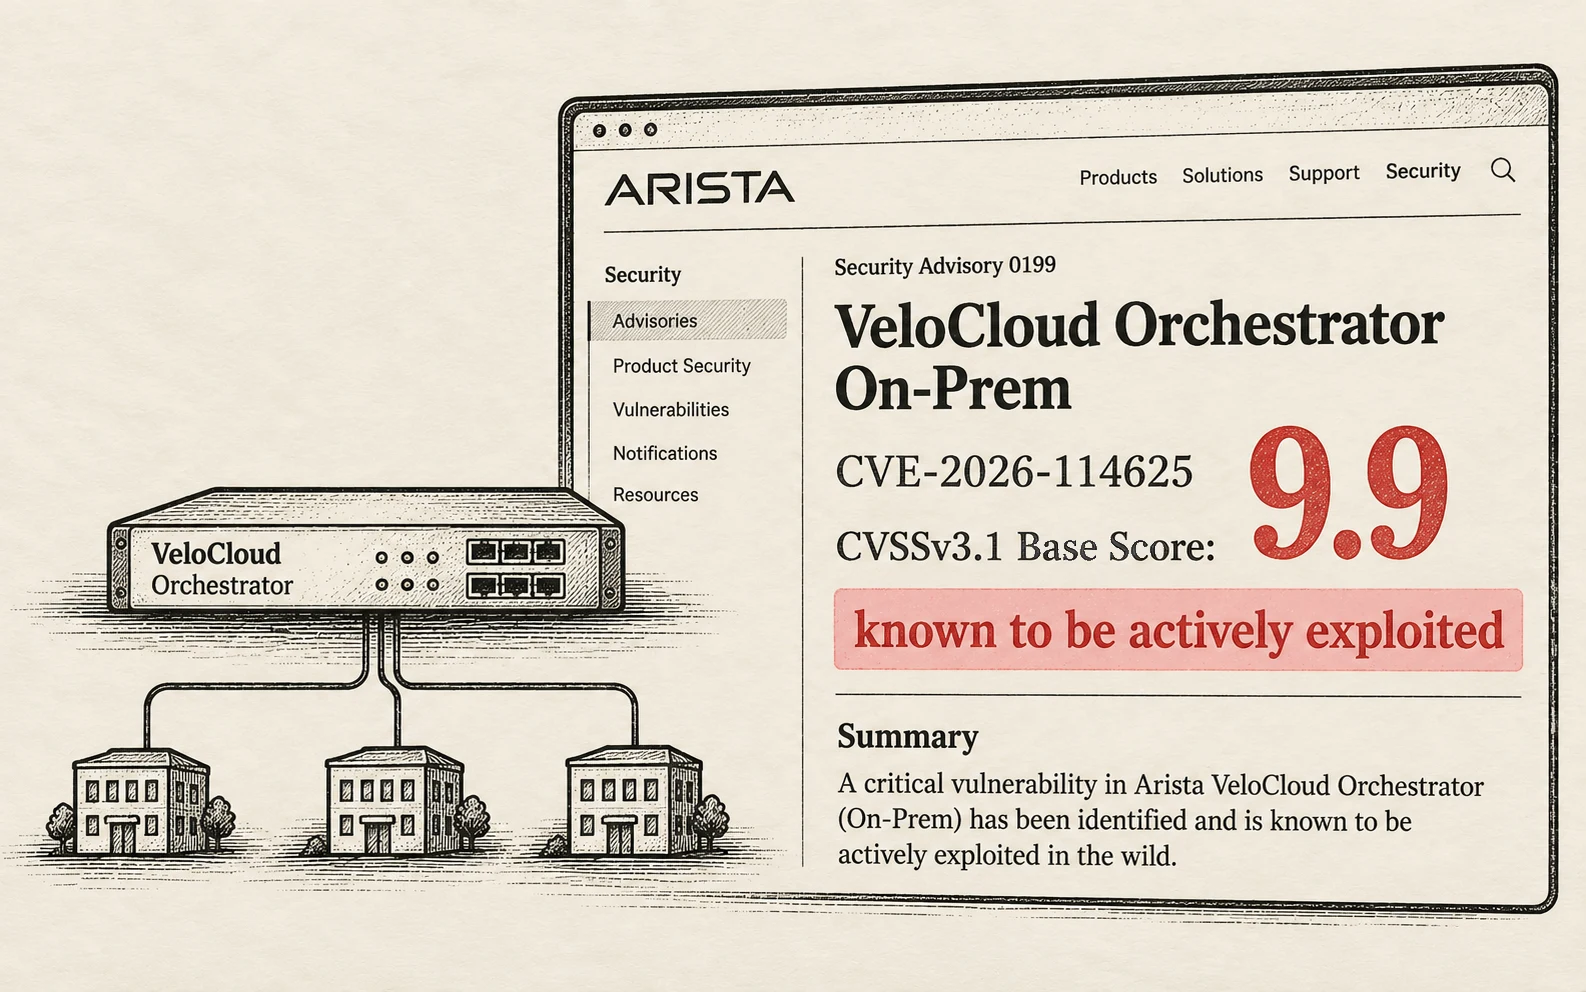
Arista Networks said on the 22nd of October 2026 that attackers exploit a SQL injection in its VeloCloud Orchestrator, rated 9.9 of 10. Any logged-in user can become superuser; on-premises owners should update to 5.2.3.18, 6.1.3.10 or 6.4.2.12.
 Arista's VeloCloud Orchestrator, CVSS 9.9
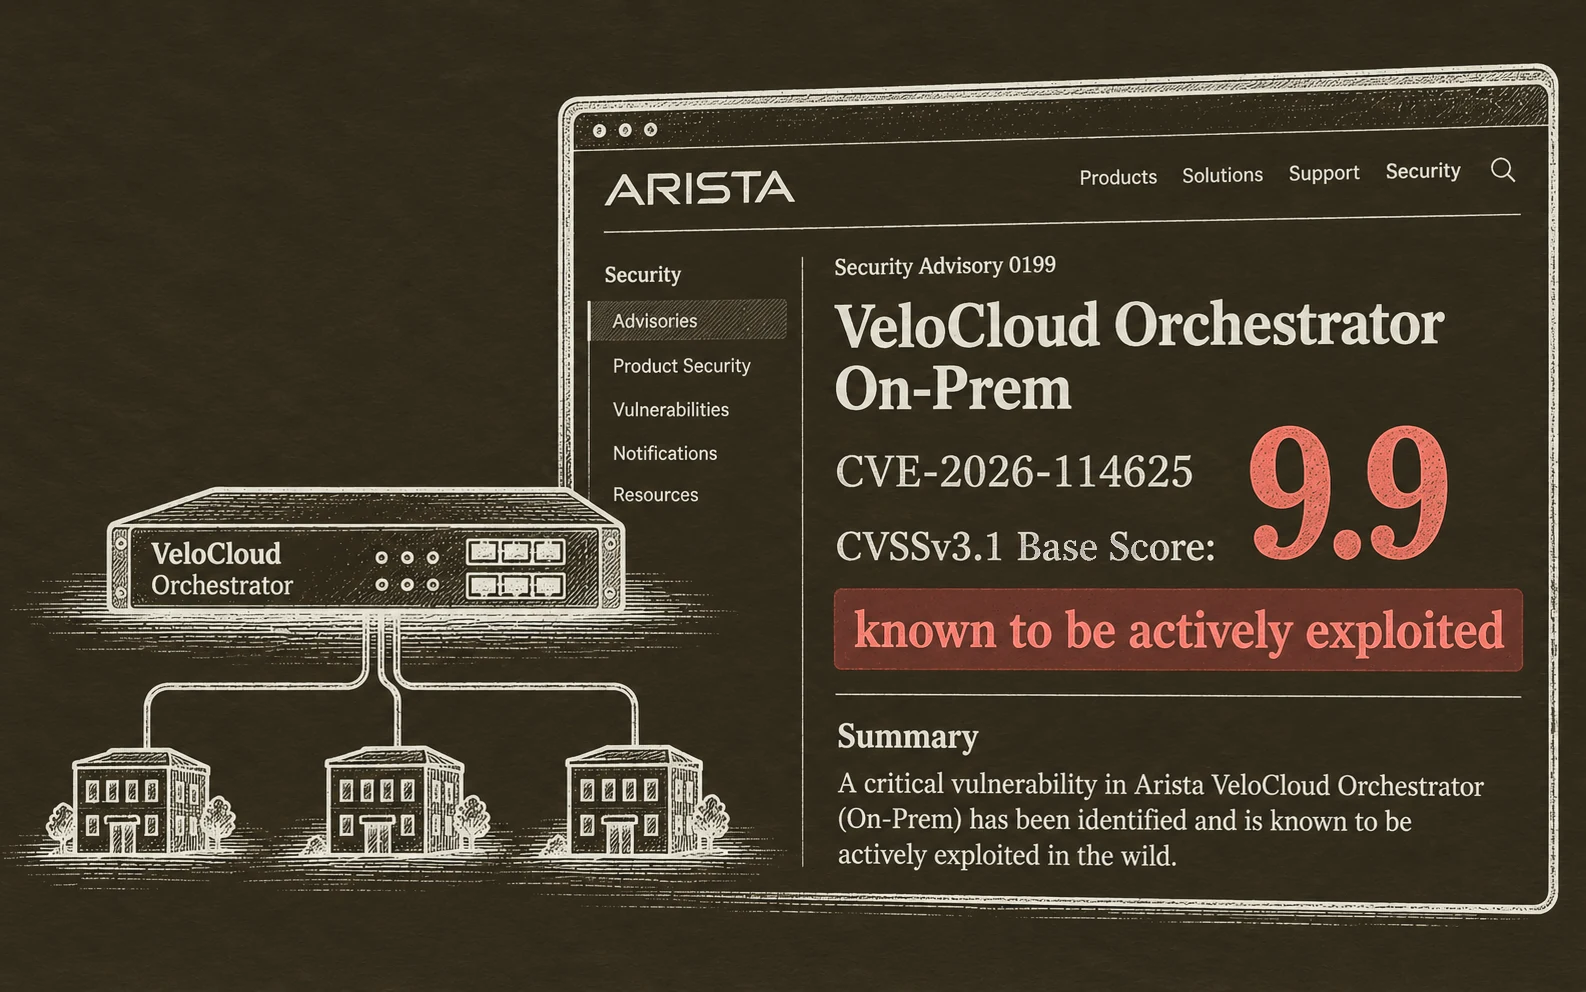
Attackers are using a new flaw in Arista Networks' VeloCloud Orchestrator, Arista said on the 22nd of October 2026. The bug, CVE-2026-114625, is rated 9.9 out of 10 in its advisory 0199.
Any user with a login can become a "superuser operator", the top account, the advisory says. Fixes are in 5.2.3.18, 6.1.3.10 and 6.4.2.12.
SD-WAN: one control panel for every office link
SD-WAN links a company's offices and cloud apps over plain internet lines. One central program decides which line each bit of traffic takes.
Arista's VeloCloud Orchestrator is that program, the panel that sets up the box in each branch. Arista bought VeloCloud from Broadcom on the 30th of June 2025, its filings say.
Below we break down who is affected, the versions and what to do now
The flaw is a SQL injection, a trick that hides database orders inside normal text, the advisory says. The attacker needs the web page and any login.
Even the lowest role, Enterprise Read Only, is enough, Arista wrote. "VCO is exposed by default," the advisory says.
Owners who run the Orchestrator on their own servers must update. Arista's Hosted and Dedicated versions are already patched, it says.
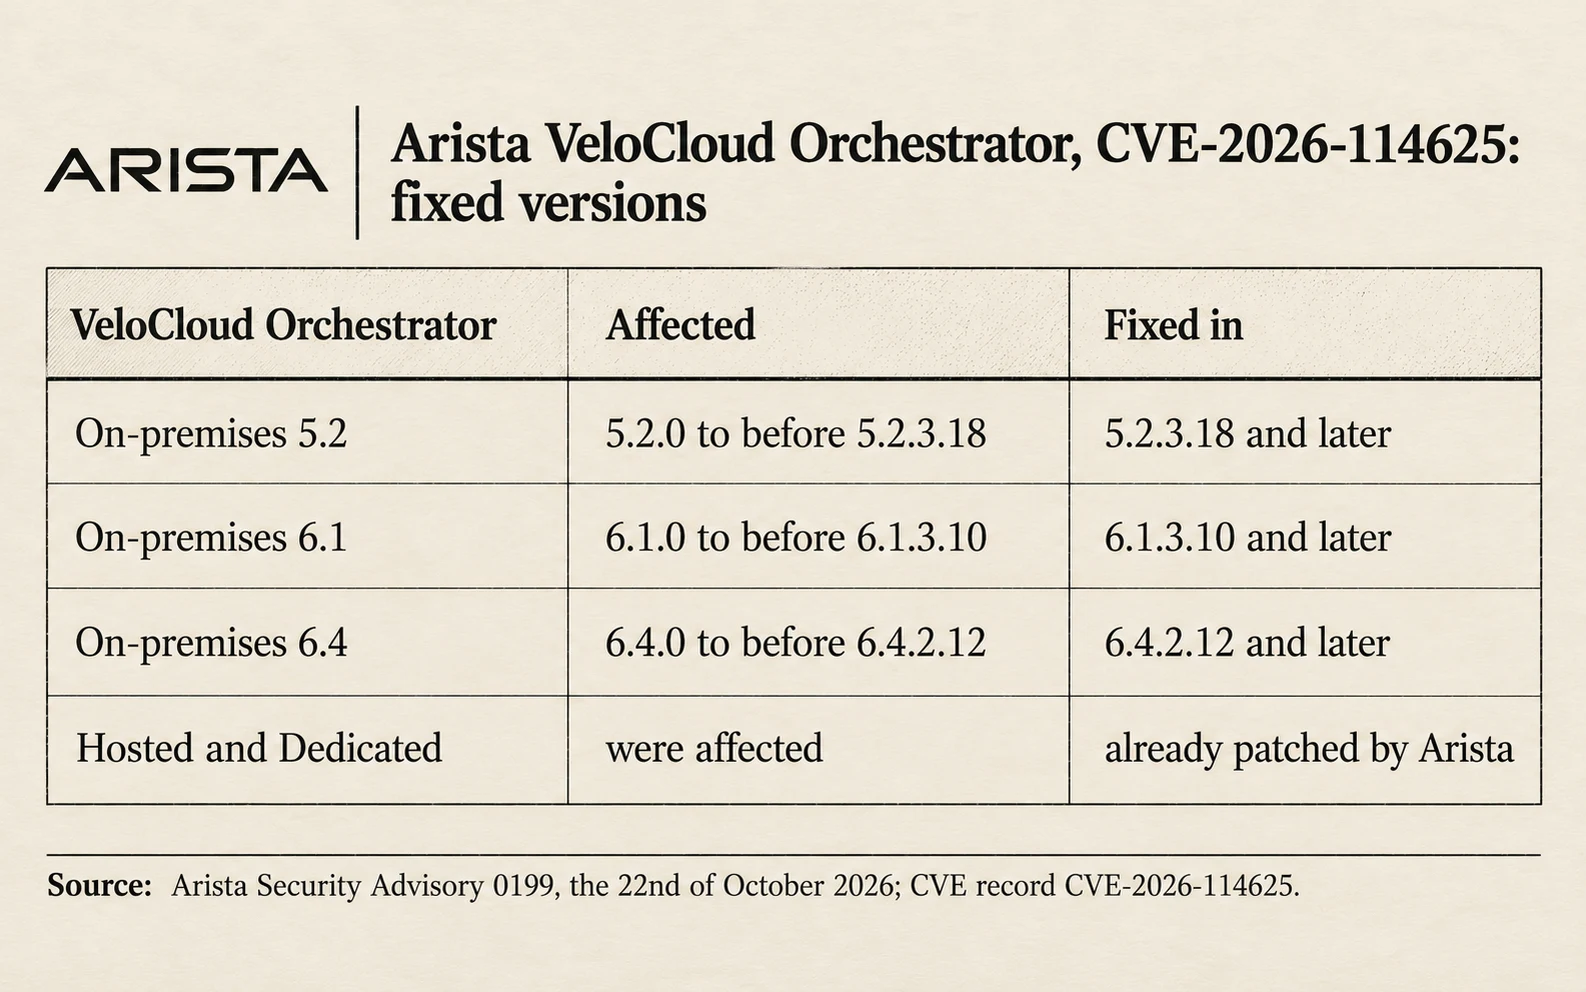
Until then, Arista asks owners to open the web page to trusted admin networks only. It named two attack addresses to block: 74.82.197.86 and 38.54.50.151.
Owners should also check logs for odd web requests and new admin changes, Arista wrote.
Third exploited Orchestrator flaw since the 27th of July 2026
Arista told of two more flaws in use on the 27th of July and the 22nd of September 2026. Neither needed a login, its advisories 0144 and 0183 say.
CISA, the US cyber agency, lists both as flaws in use by attackers.
What is confirmed and what is not
Arista confirmed the attacks but named no attacker and no count of victims. BleepingComputer reported the same two addresses on the 22nd of October.
CISA's list of the 21st of October did not yet hold the new bug on the 23rd.
Key facts
Disclosed by Arista on the 22nd of October 2026 in advisory 0199.
CVE-2026-114625, a SQL injection rated 9.9, already exploited.
Any logged-in user, even read-only, can become superuser.
Fixed in 5.2.3.18, 6.1.3.10 and 6.4.2.12.
Third exploited Orchestrator flaw since July 2026.
Source: Arista Security Advisory 0199