Cursor says 1 stolen key opened its breach
Cursor, the AI code editor, said a breach let hackers spread fake copies of a Claude Code add-on to developers. Up to 5,000 developers may have received them, BleepingComputer reported on the 14th of November 2026.
 Cursor explains its breach
Cursor, the AI code editor, said a breach let hackers spread fake copies of a Claude Code add-on to developers. Up to 5,000 developers may have received them, BleepingComputer reported on the 14th of November 2026.
The hackers first took an access key stored at Fireworks AI, a company Cursor used to run AI models. The key opened a storage space that Cursor shared with Fireworks.
What was inside
The storage held old records of AI coding sessions, mostly from 2025, BleepingComputer reported. They came from users who had not turned on Privacy Mode.
Some records held passwords and keys for other services. The hackers used them to get into more Cursor systems.
The fake add-on
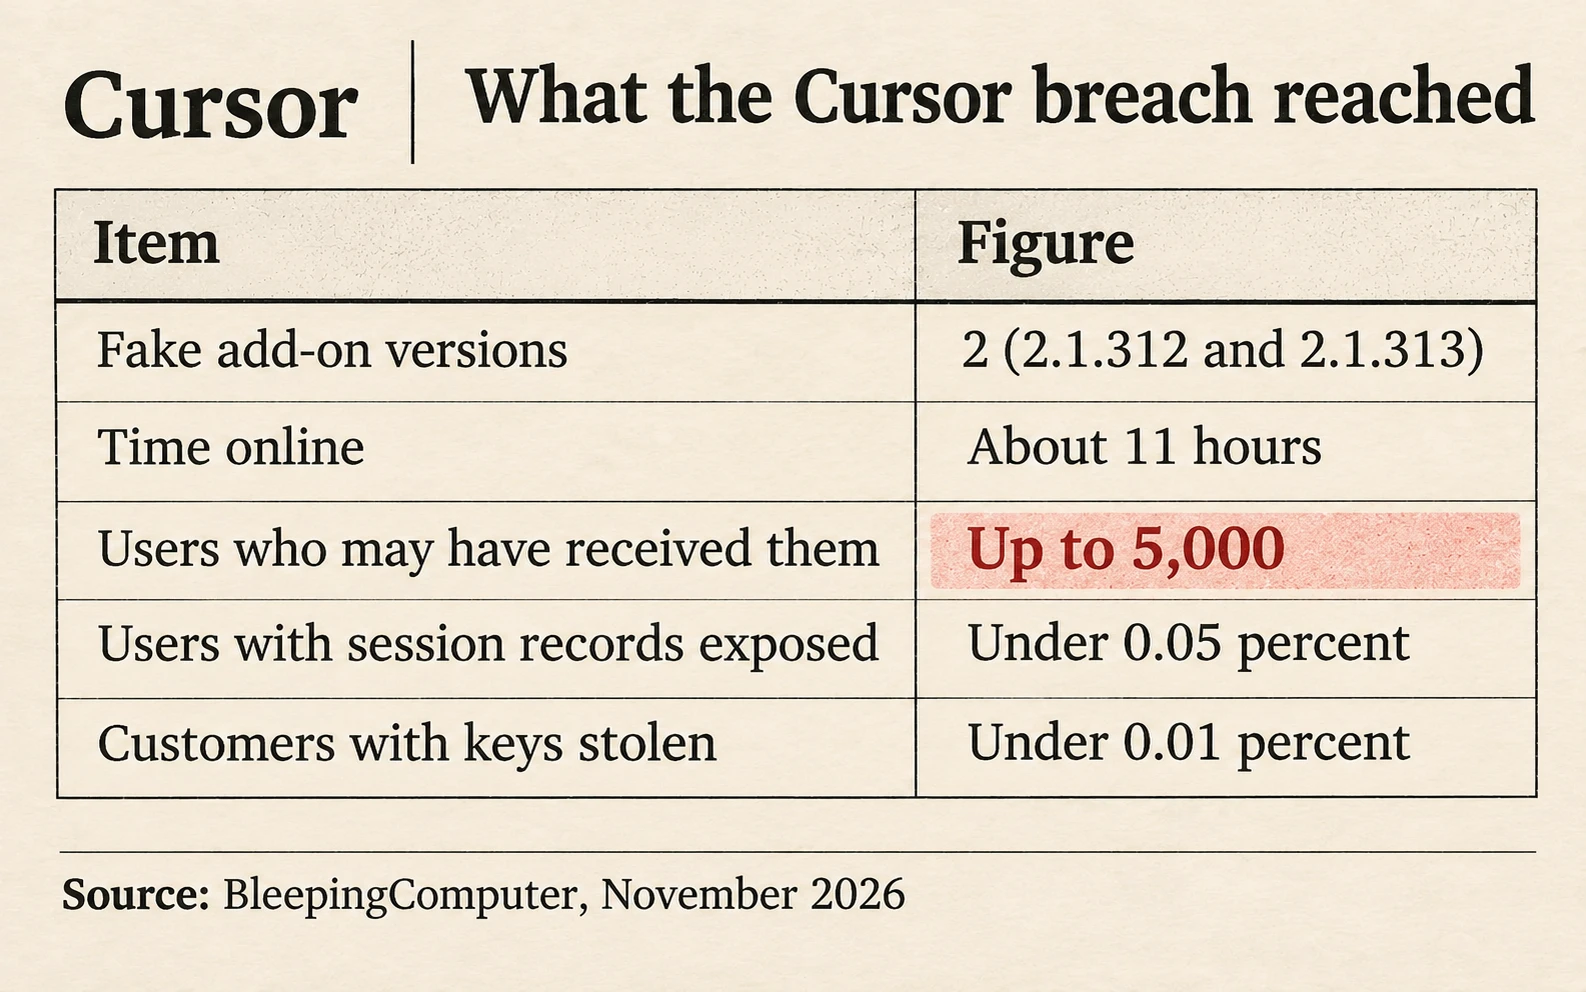
On the 29th of October, the hackers placed two fake versions of Anthropic's Claude Code add-on in Cursor's add-on store. They stayed up for about 11 hours.
The fake versions tried to open a hidden back door into each computer, BleepingComputer reported. Researchers found coding errors that likely stopped it on many Windows and Mac computers.
What else was taken
The hackers also took old source code, some support emails, usage figures and customer contact details, Cursor said. Its main systems, official app releases and customer code were not touched.
Cursor said it has moved all AI traffic away from Fireworks and rebuilt its add-on store.
Below we break down the numbers
Fewer than 0.05 percent of users had session records exposed, Cursor said. Fewer than 0.01 percent had keys stolen, which is at most one customer in 10,000, by our arithmetic.
Key facts
Cursor said a stolen Fireworks AI key started the breach.
Two fake Claude Code add-on versions were online for about 11 hours.
Up to 5,000 developers may have received them.
Cursor moved all AI traffic away from Fireworks.