eMudhra key was the number 4: 8 certs blocked
Browsers began blocking eight certificates of the Indian certificate authority eMudhra on the 17th of October 2026, after their secret keys turned out to be tiny numbers. Browsers are covered; servers, phones and tools with their own root lists need updates.
 eMudhra's 8 intermediate keys, blocked
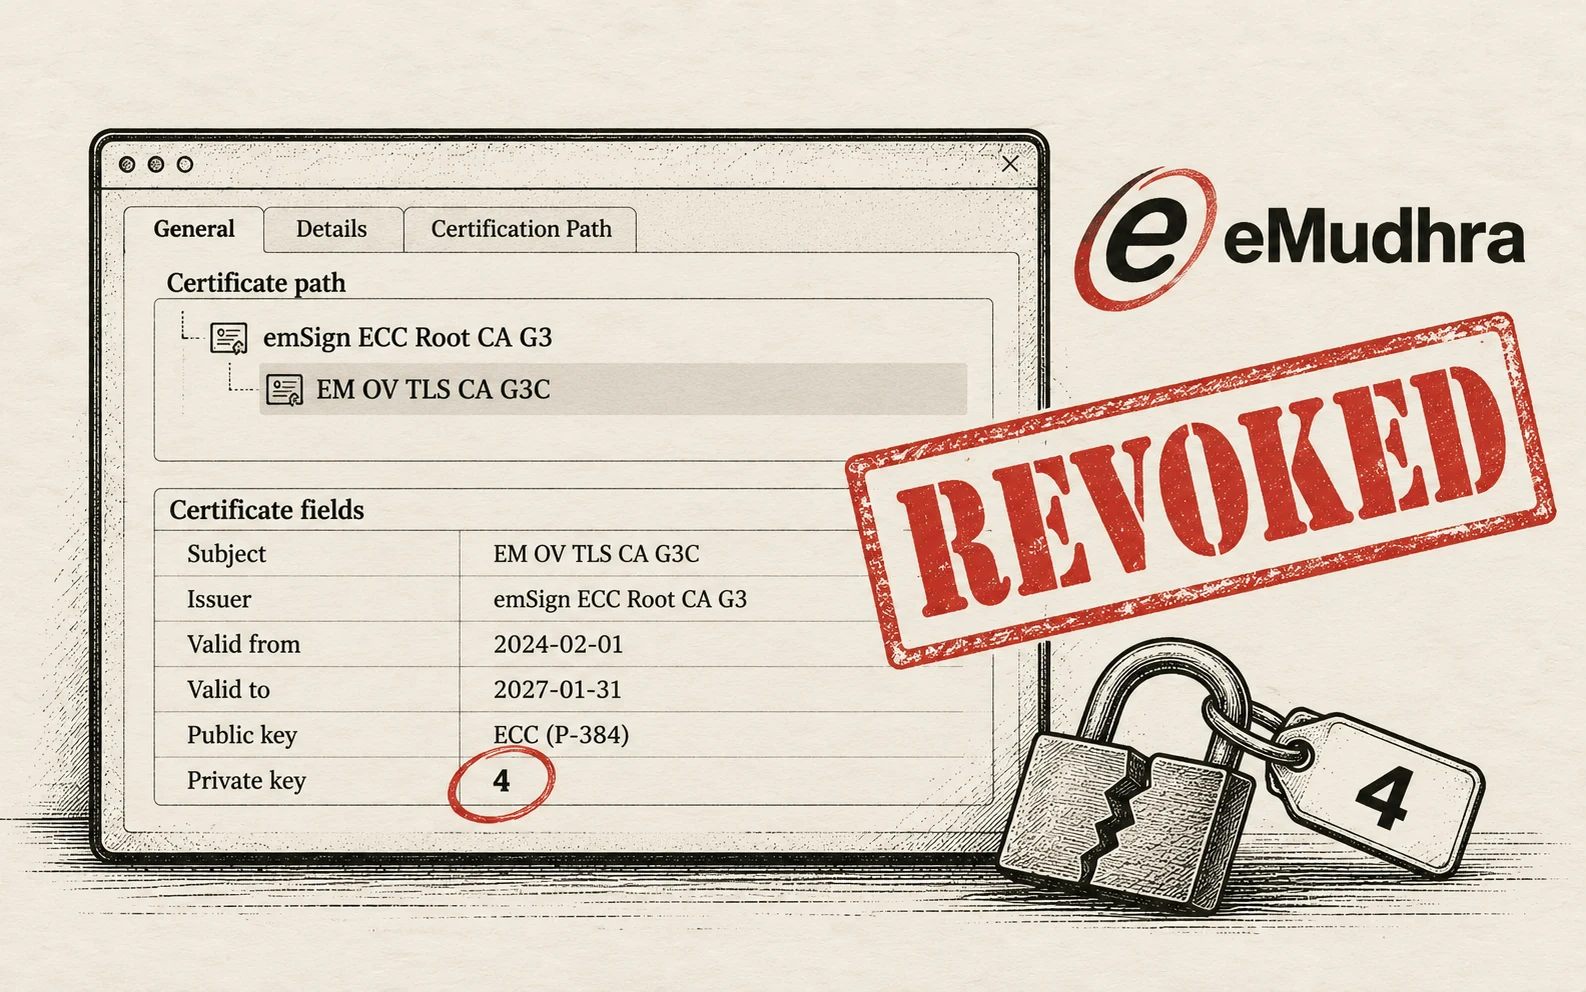
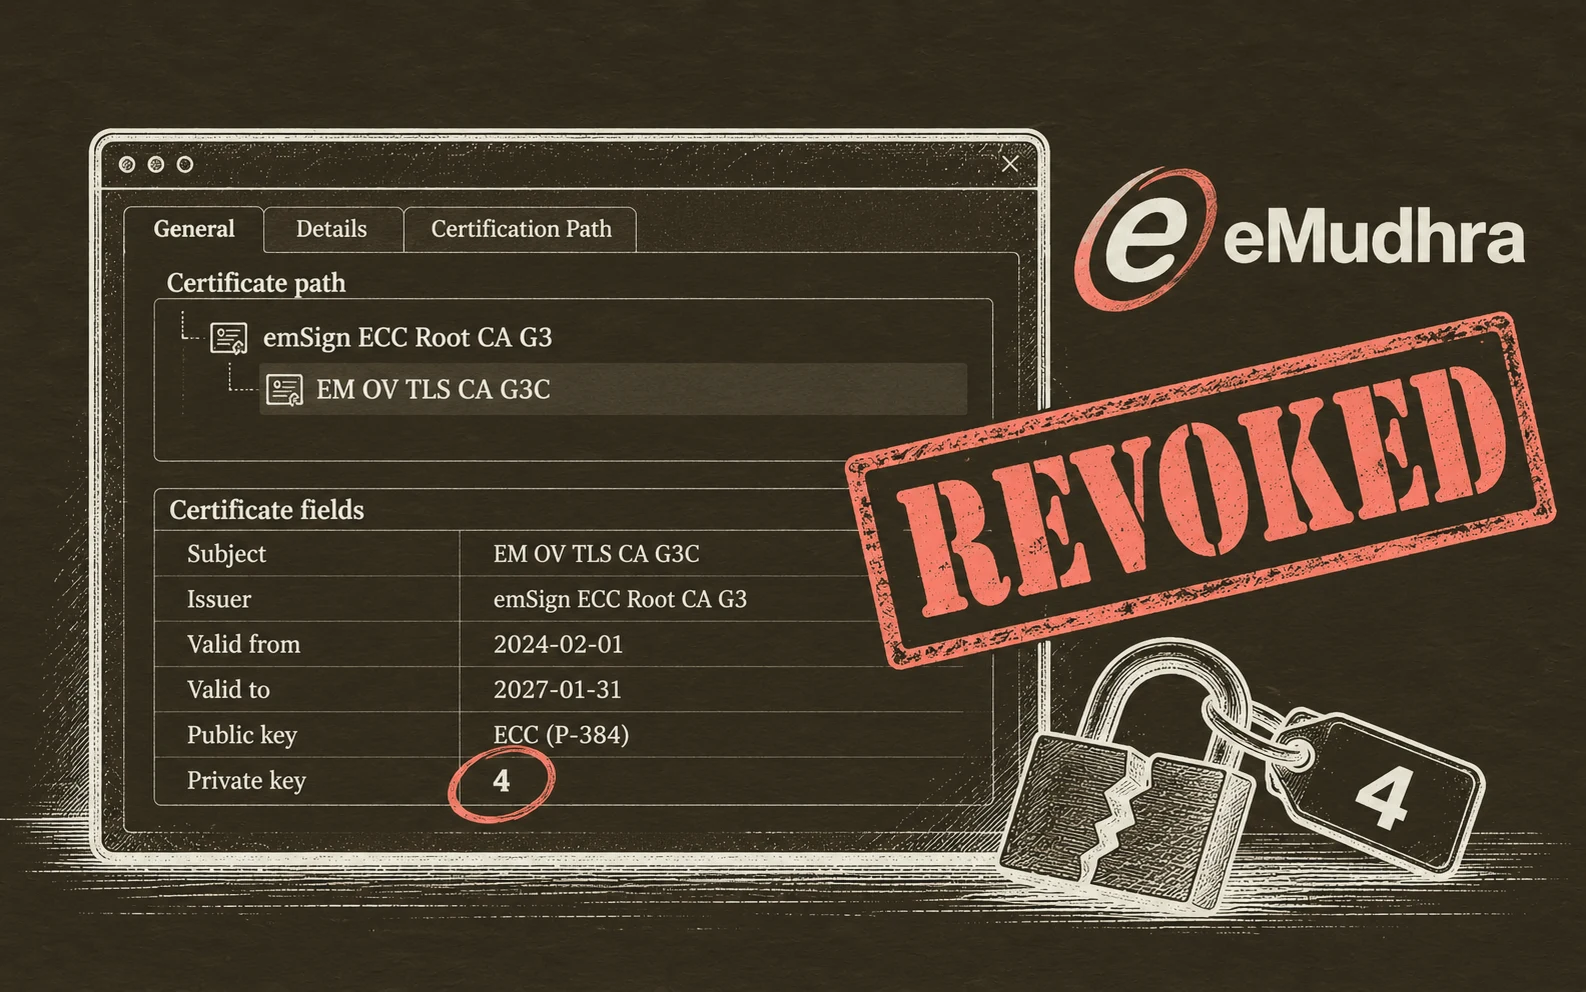
Eight certificates of eMudhra, an Indian certificate authority, had compromised secret keys, Mozilla wrote on the 20th of October 2026. One key was the number 4, researcher Scott Helme wrote that day.
A certificate authority is a company browsers trust to vouch for websites. Its private key is the secret number it signs with, so its holder can fake any website's certificate.
Chrome, Firefox, Microsoft and Apple now block the 8 certificates
Chrome blocked them on the 17th of October, 100 minutes after the report, Google wrote. Firefox's block reached users that day without an update, Mozilla wrote.
Microsoft blocks them since the 20th and Apple since the 22nd, says a tracking site run by Dennis Jackson of Mozilla. The firm revoked all eight on the 18th, eMudhra's statement says.
Below we break down the 8 keys, the cause and what to do now
A proper key of this type has about 10 to the power of 115 values to pick from, Helme wrote. The eight keys were 4, 56, 66, 115, 155, 156, 230 and 237.
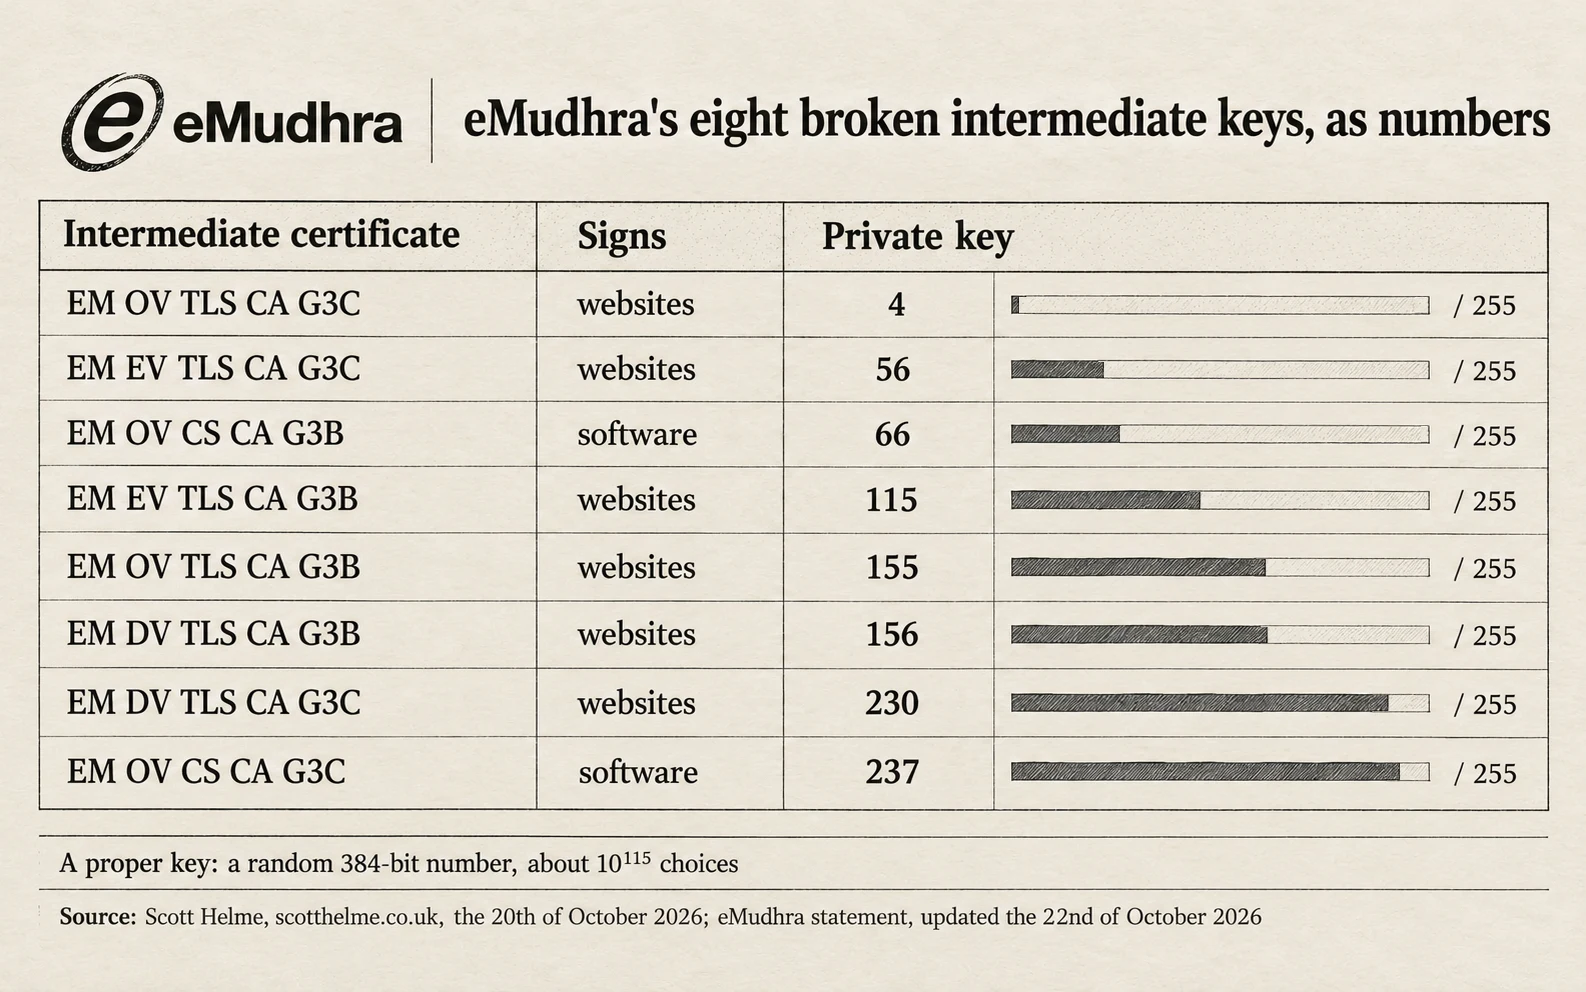
Helme found all of them in under a second on his laptop, he wrote. Six certificates vouch for websites and two for software.
eMudhra wrote that a step in its key setup of the 30th of April 2025 "produced a second, weak set of keys".
Chrome drops eMudhra's root, emSign ECC Root CA G3, on the 27th of October, Google wrote. Sites under it "must immediately acquire and install a new TLS certificate."
Restarting an Android phone loads Google's fix at once, Google wrote. Many tools outside browsers "require software updates," Jackson's site says, and it offers a test page.
What is confirmed and what is not
None of the eight ever signed a website certificate, eMudhra wrote on the 22nd, citing public certificate logs.
"This will be a massive cleanup job, bigger than Heartbleed," Filippo Valsorda, a Go cryptography expert, told Ars Technica, The Next Web reported. Heartbleed was a 2014 flaw that leaked server secrets.
Key facts
Reported on the 17th of October 2026: eight eMudhra keys were compromised.
One key was the number 4.
Chrome, Firefox, Microsoft and Apple block them.
Chrome drops the emSign root on the 27th of October.
Update browsers, phones and tools with their own root lists.