Fake Claude Code add-on reached 5,000 coders
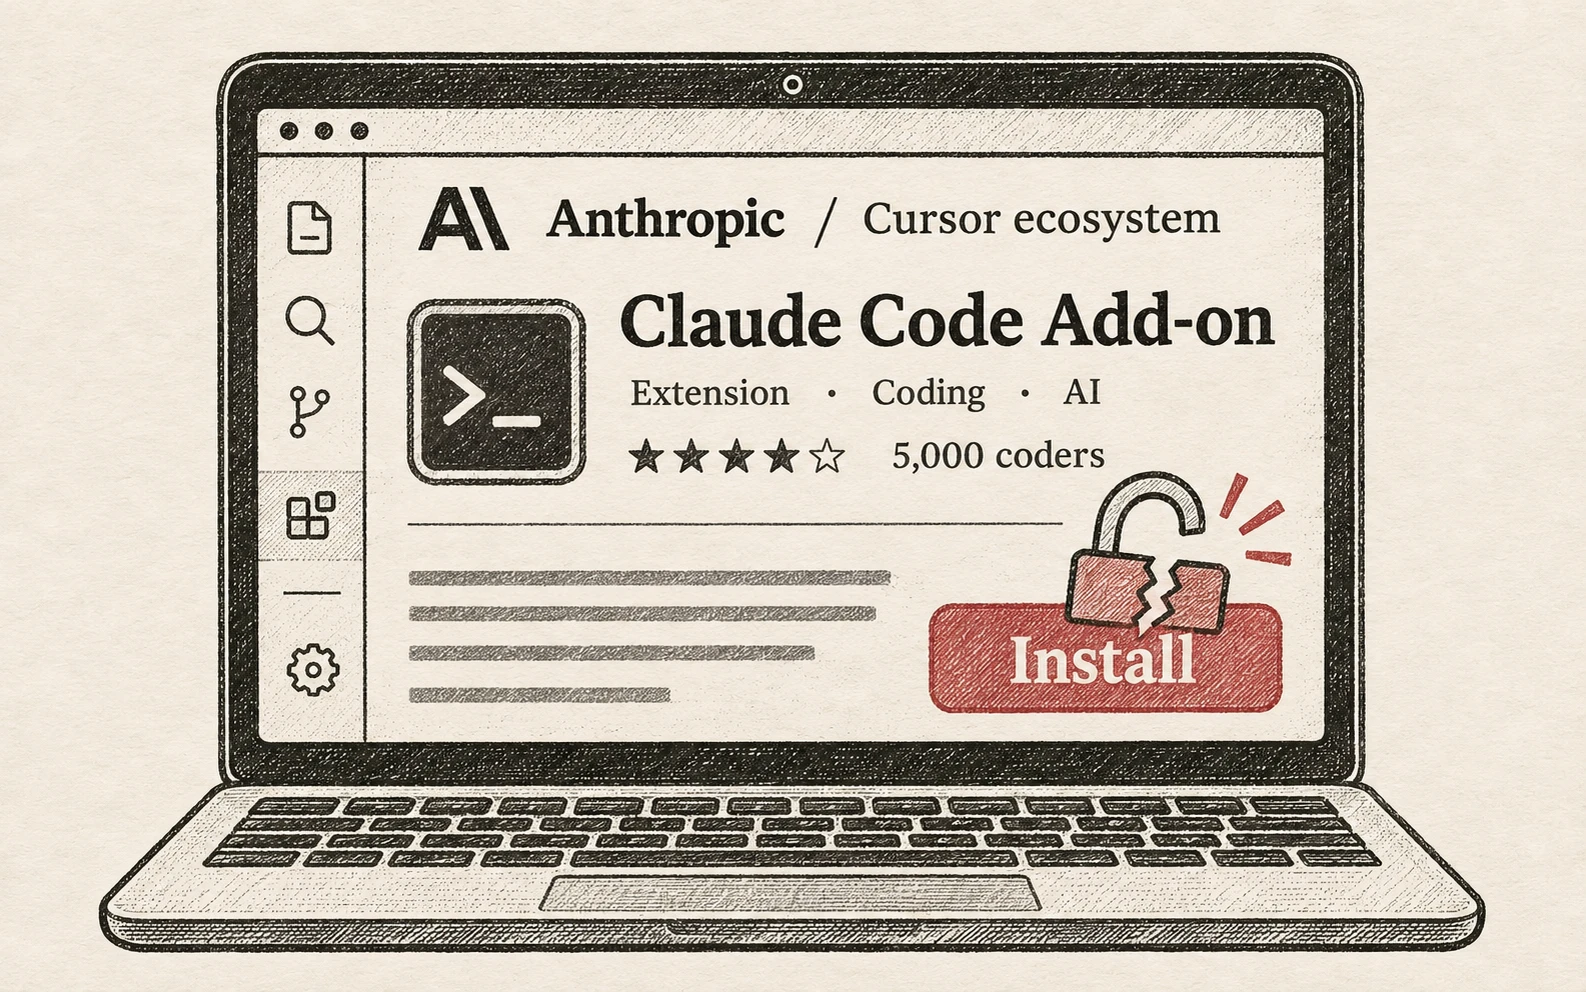
A fake copy of Anthropic's Claude Code add-on sat in Cursor's add-on store for about 11 hours. It tried to plant a secret login key on developers' computers, Cursor said.
 Anthropic's Claude Code in Cursor
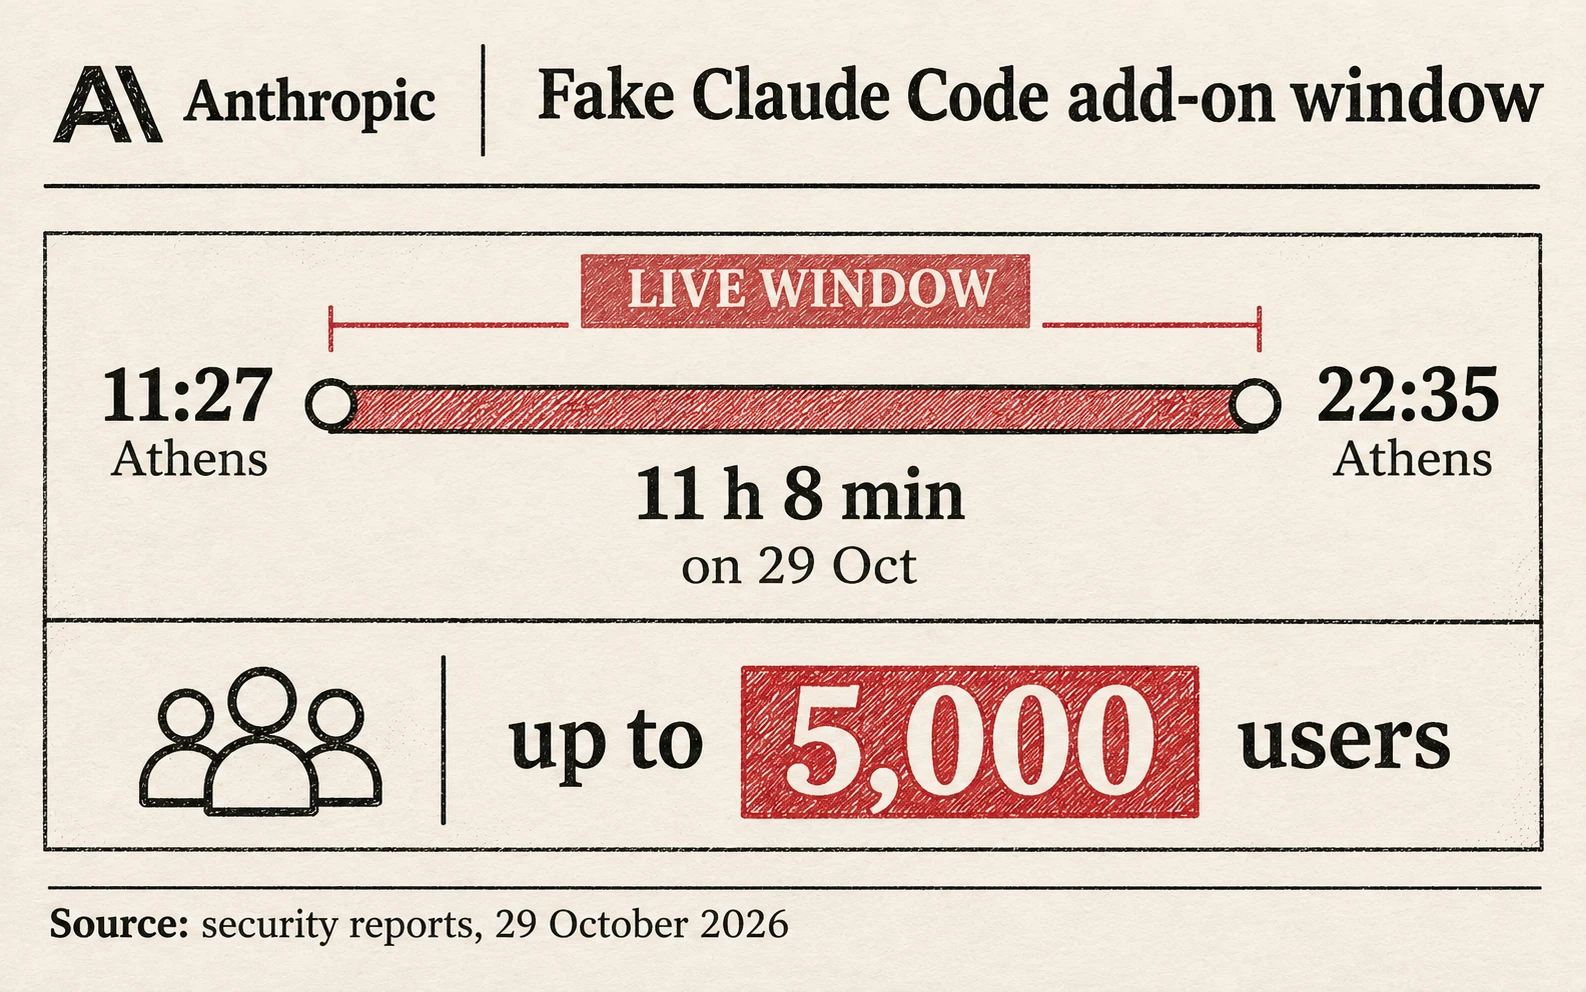
A fake copy of Anthropic's Claude Code add-on sat in Cursor's add-on store for about 11 hours on the 29th of October 2026. It reached at most 5,000 users, Cursor said, according to security firm StepSecurity.
Cursor is an AI coding app. The bad versions, numbered 2.1.312 and 2.1.313, were for Mac and Windows computers, Cursor said.
What the fake add-on did
The add-on tried to plant a secret key that lets an attacker log in from far away. It also sent the computer's name and other details to the attacker, Cursor said.
On most computers the remote login step failed, because it needs administrator rights. The attacker's server has since been shut down, Cursor said.
What Cursor did
Cursor removed the add-on and took its whole store offline. It changed its own security keys, rebuilt the store and brought it back.
Anthropic did not make or publish the bad versions, Anthropic said. Copies on Anthropic's own channels were safe, StepSecurity reported.
What users should do
Anyone who installed either version from Cursor's store that day should run Cursor's cleanup script. Removing the add-on alone does not remove the attacker's hidden files, StepSecurity said.
Users should also change passwords and keys that the computer could reach, Cursor said.
Below we break down the 11 hours
The add-on went live at 2:27am Pacific time and came down at 1:35pm. That is 11 hours and 8 minutes, by our arithmetic.
In Athens time, that ran from 11:27 to 22:35 on the 29th of October.
Key facts
Fake versions 2.1.312 and 2.1.313 of Claude Code sat in Cursor's store.
They were live for about 11 hours on the 29th of October 2026.
At most 5,000 users received them, Cursor said.
Affected users should run Cursor's cleanup script and change passwords.
Source: Cursor security notice