LiteLLM 1.107.0 hacked: rotate every AI key
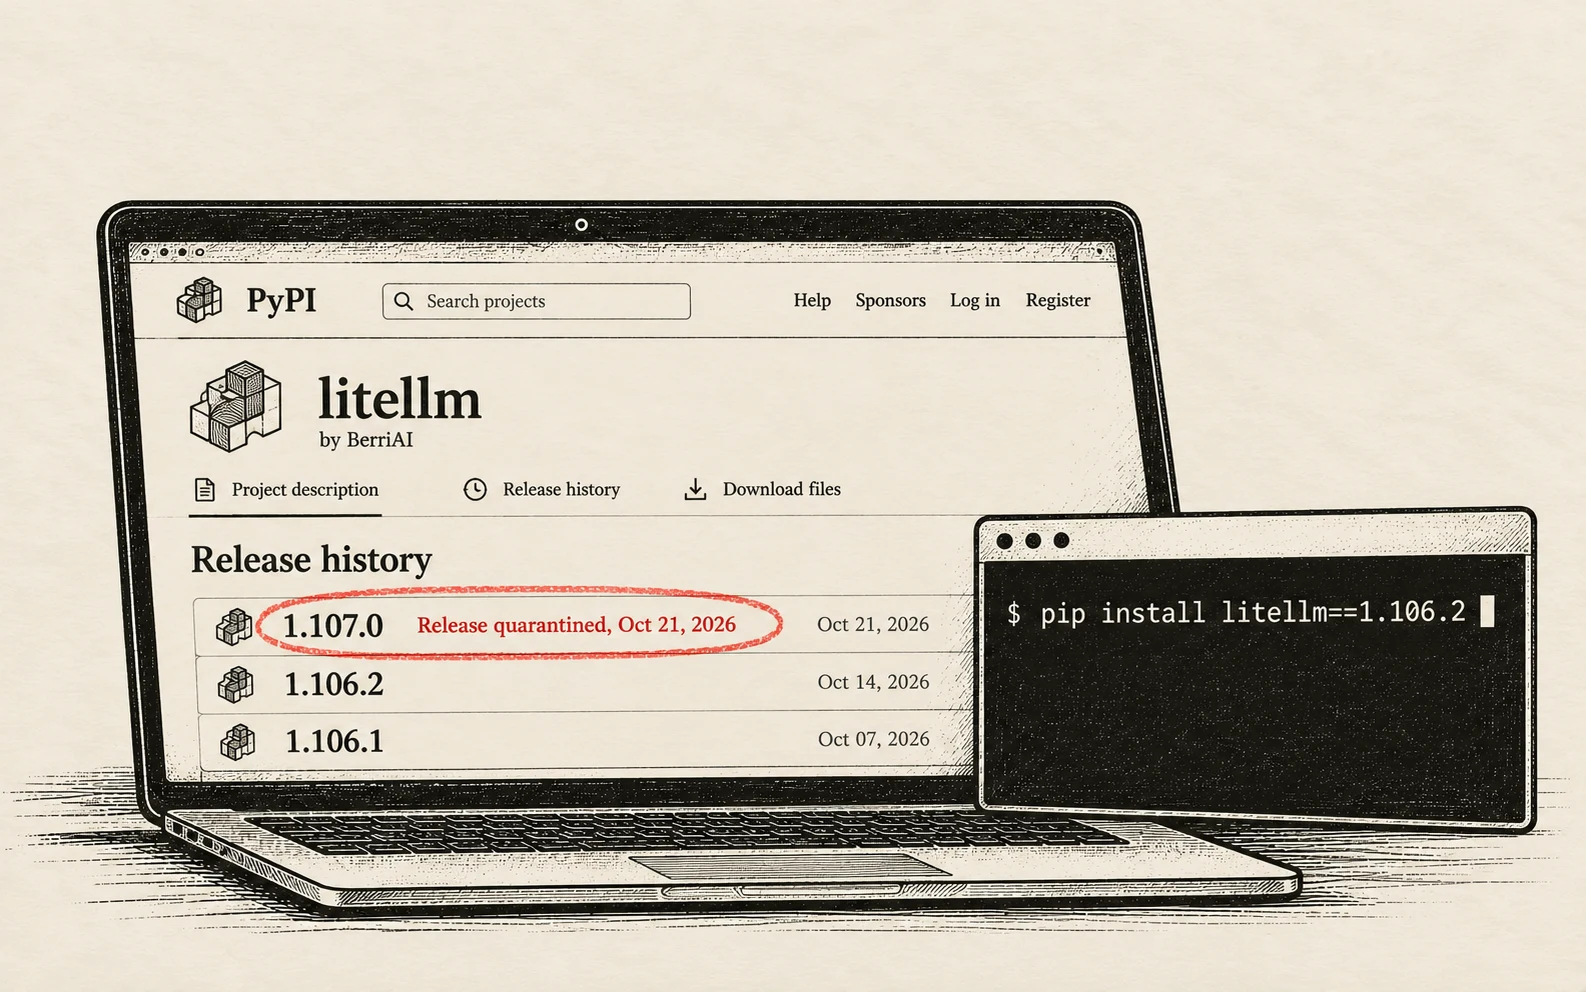
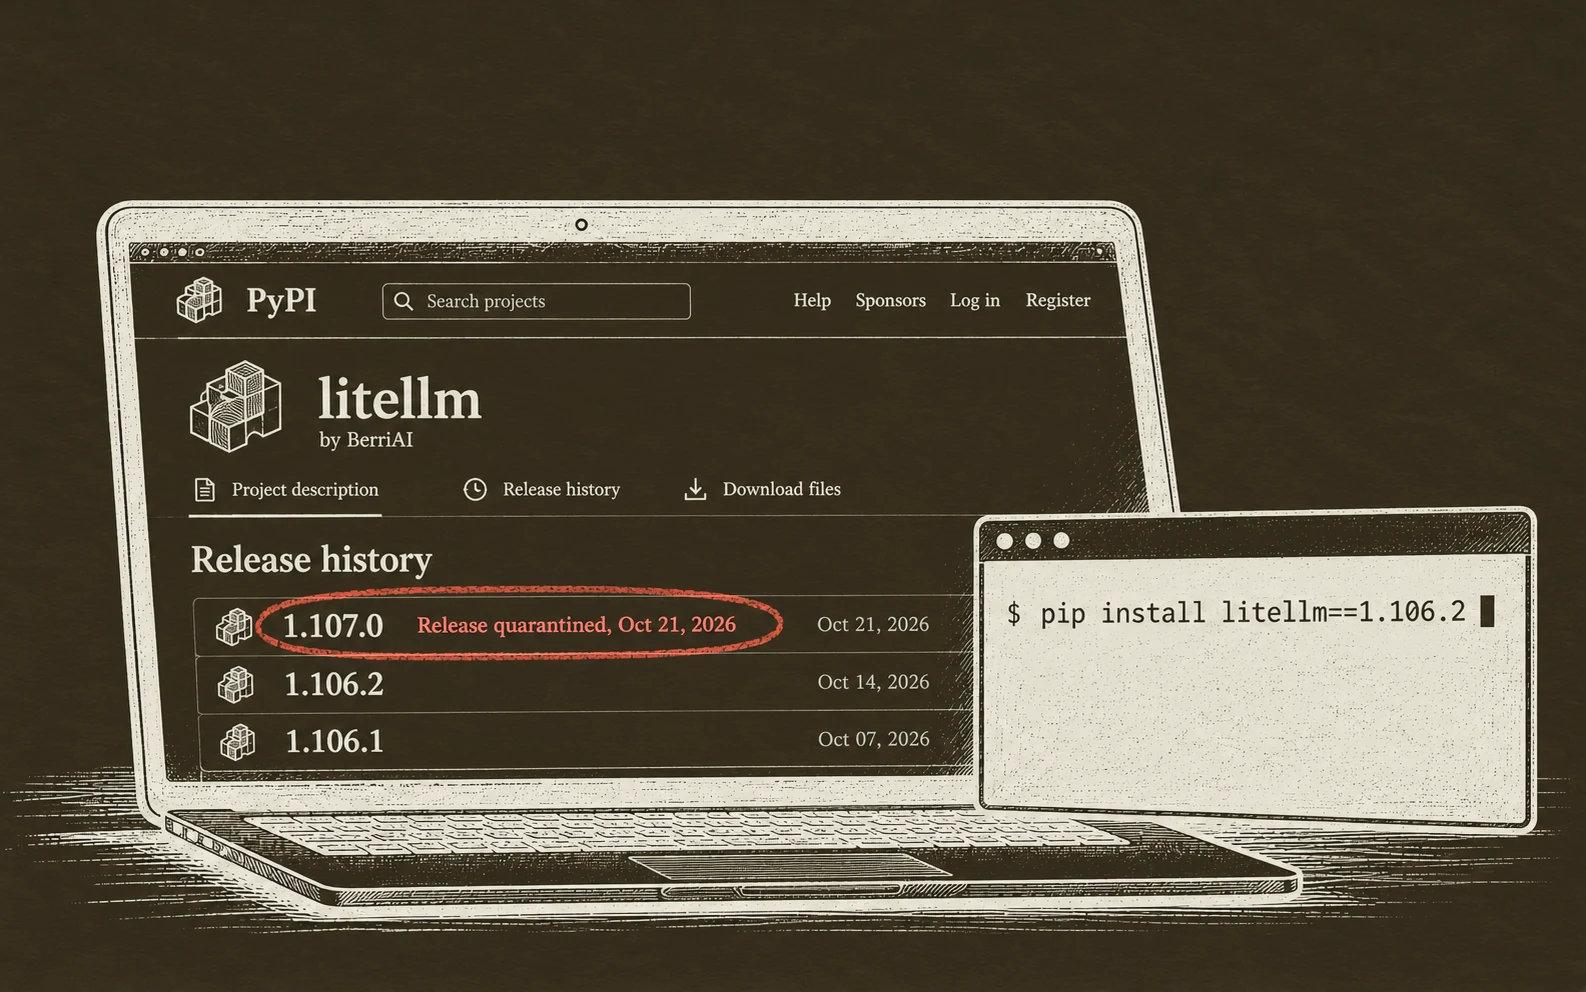
A poisoned version 1.107.0 of BerriAI's LiteLLM sat on PyPI and Docker for up to 2 and a half hours on the 21st of October 2026. Anyone who installed it should pin 1.106.2 and rotate every cloud and AI key.
 BerriAI's LiteLLM 1.107.0 poisoned
A poisoned version 1.107.0 of BerriAI's LiteLLM went out on the 21st of October 2026, the company said that day. It stole keys and let attackers run their own code.
LiteLLM is a Python tool that links apps to many AI model makers. It gets 92 million downloads a month, BleepingComputer reported on the 22nd.
Below we break down the bad version, the hours and what to do
All seven install files of 1.107.0 were live on PyPI, the Python package store, from 11:39 to 13:23 UTC, BerriAI wrote. Docker Hub tags v1.107.0, latest, main-latest and main-stable served a bad image from 11:46 to 14:20 UTC.
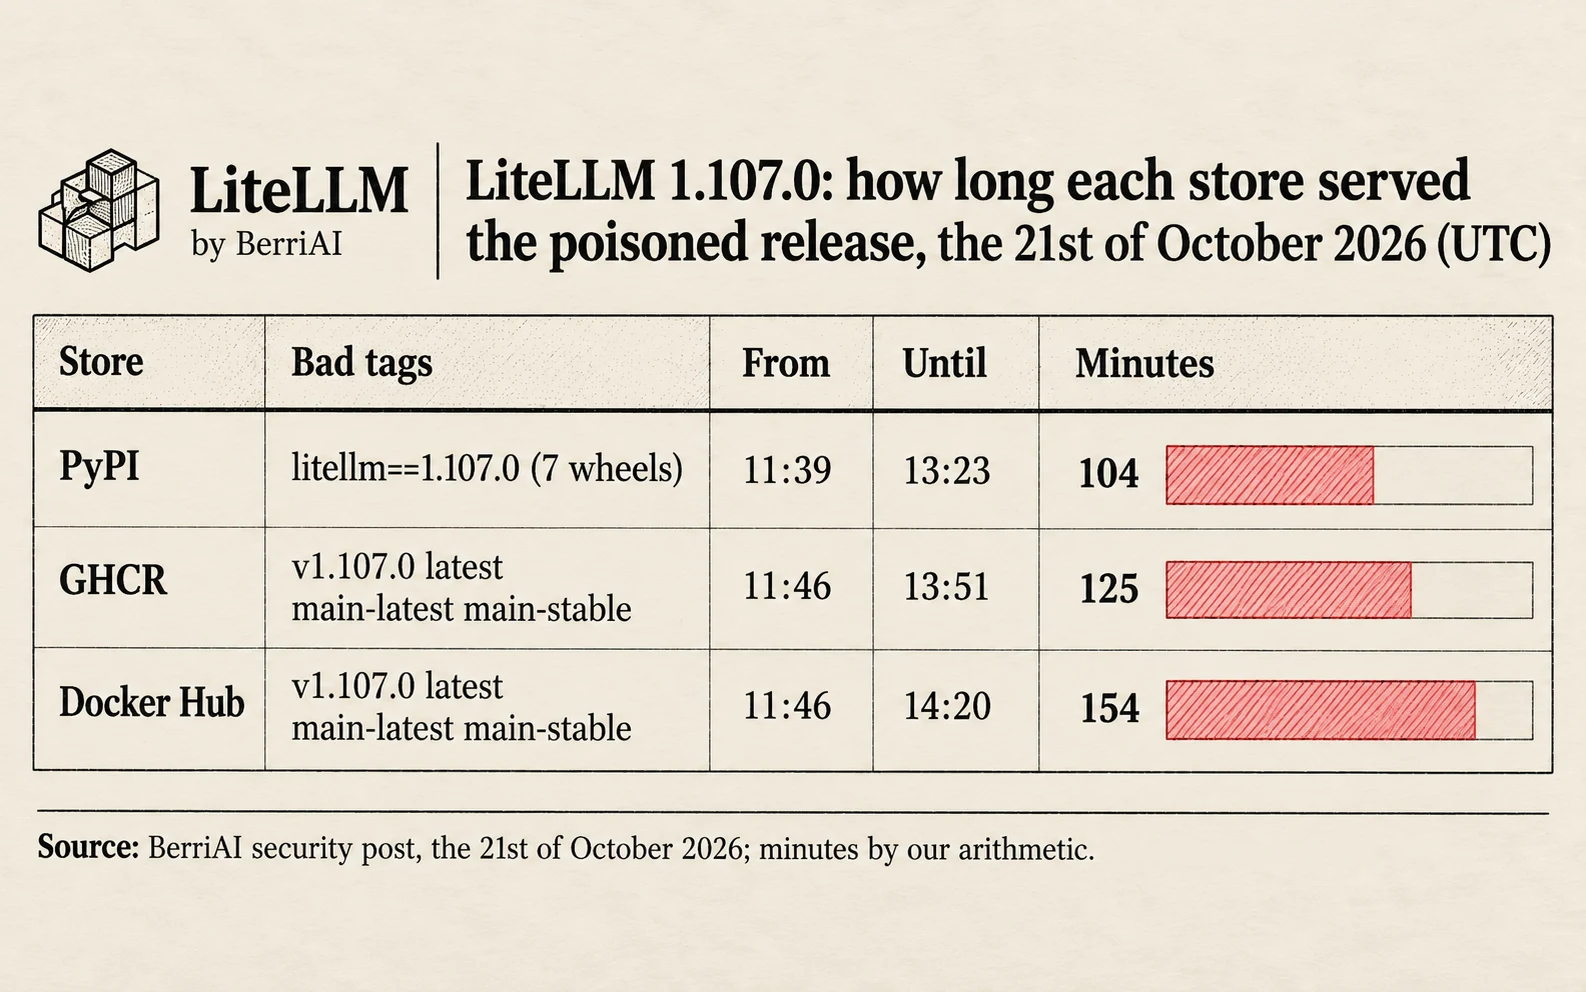
You are affected if you installed LiteLLM without a fixed version, or pulled those tags, in those hours. Customers on the private enterprise release were not hit, BerriAI said.
BerriAI warned against starting with pip install, since any Python start reruns the malware. Delete the added files, then reinstall litellm 1.106.2.
Rotate every cloud role, AI provider key, LiteLLM key, database password and stored secret, BerriAI wrote.
Three engineers' stolen GitHub tokens ran the release
BerriAI found an unknown user account on its internal LiteLLM server, which was open to the internet. It believes the attacker took GitHub login tokens from that server's logs.
Anthropic's Claude Code can put such a token into a reply that LiteLLM may log, BerriAI wrote. The build used a copy named Berri-AI/litellm, one hyphen off the real name, Datadog wrote on the 21st.
The malware takes cloud, AI and developer keys
Three added files run each time Python starts, Aikido Security wrote on the 21st. They take cloud keys, SSH keys, browser passwords and AI provider keys.
A remote access trojan, a hidden program that obeys a distant server, asks for new code every hour, Aikido wrote.
What is confirmed and what is not
BerriAI has not confirmed how the attacker reached its server. No source has said how many people installed 1.107.0.
Aikido says the PyPI window closed at 12:47 UTC, and BerriAI says 13:23.
Key facts
LiteLLM 1.107.0 was poisoned on the 21st of October 2026.
PyPI from 11:39 to 13:23 UTC, Docker until 14:20 UTC.
It steals cloud and AI keys.
Three engineers' GitHub tokens were stolen.
Pin 1.106.2 and rotate every key.
Source: BerriAI's LiteLLM security post of the 21st of October 2026