Node.js fixes 10 flaws, one a 9.2 Brotli RCE
The Node.js project released 26.12.1, 24.22.1 and 22.23.4 on the 21st of October 2026 with 10 security fixes. One Brotli flaw can let an attacker run code, so servers on these lines should update now.
 Node.js project fixes 10 security flaws
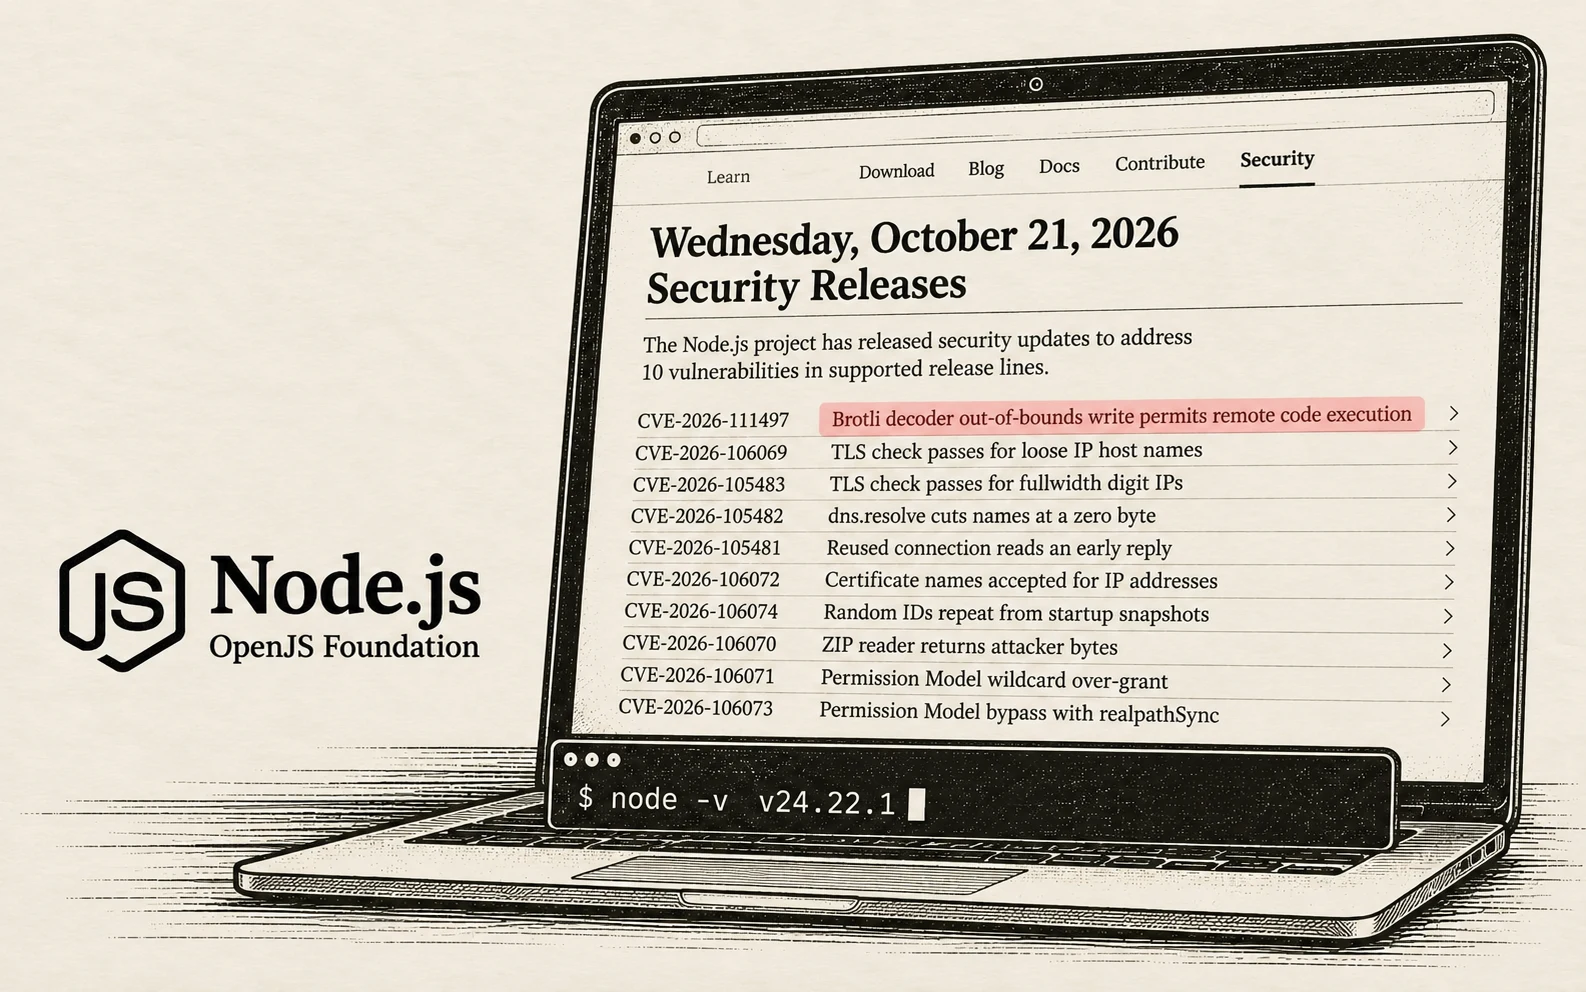
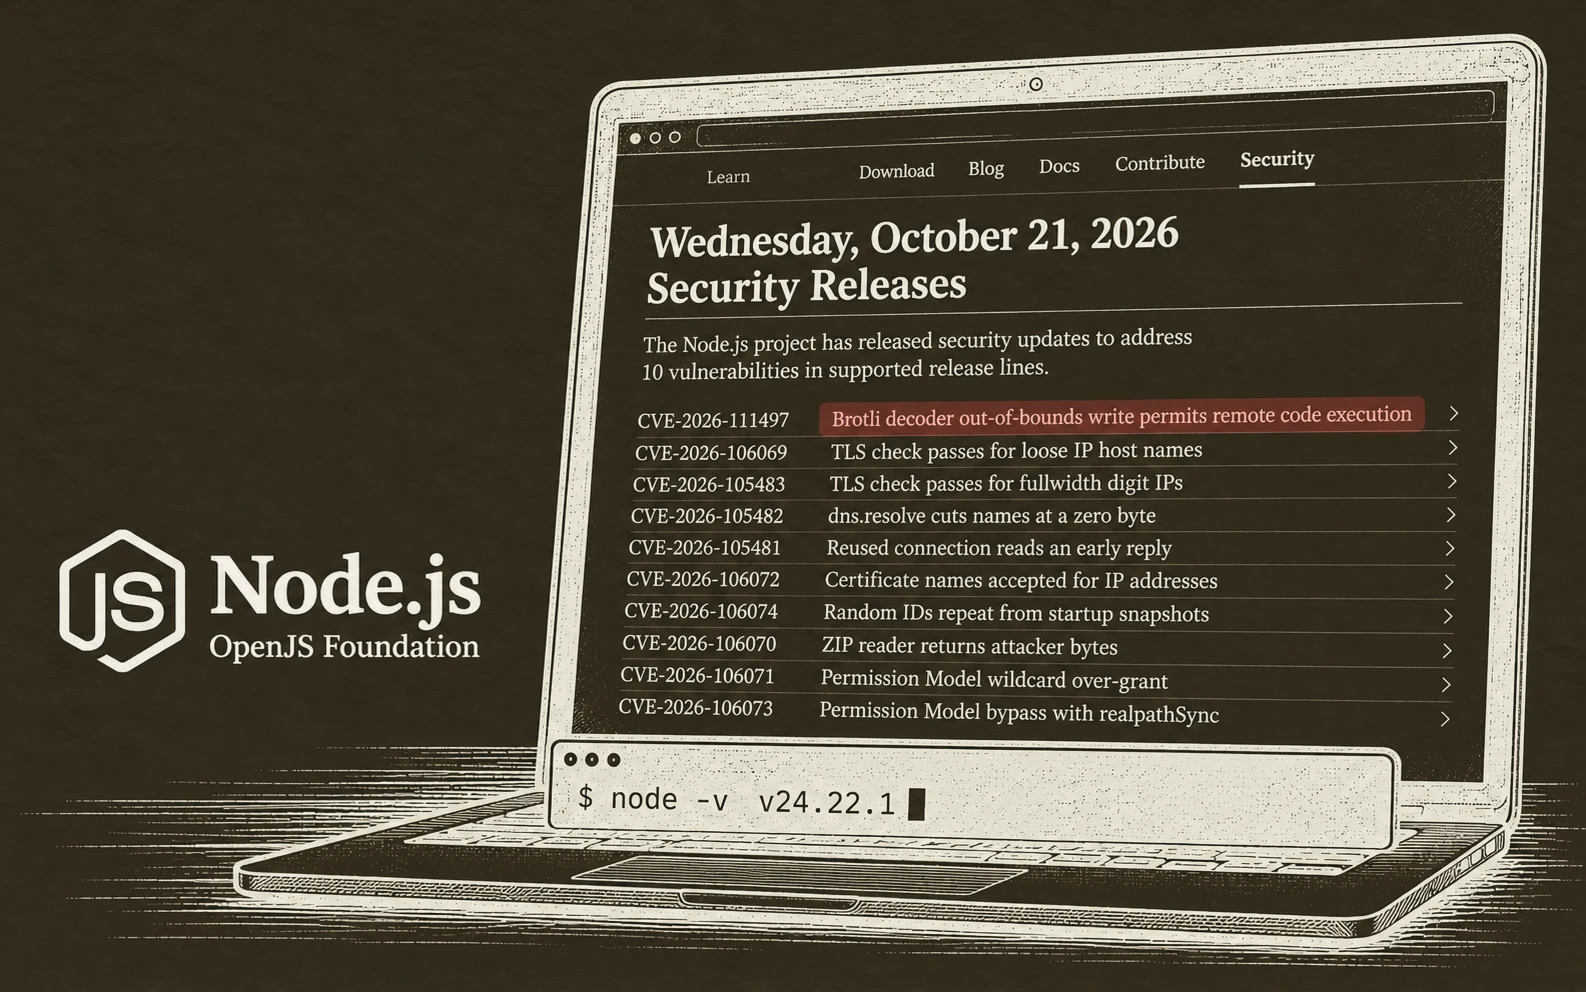
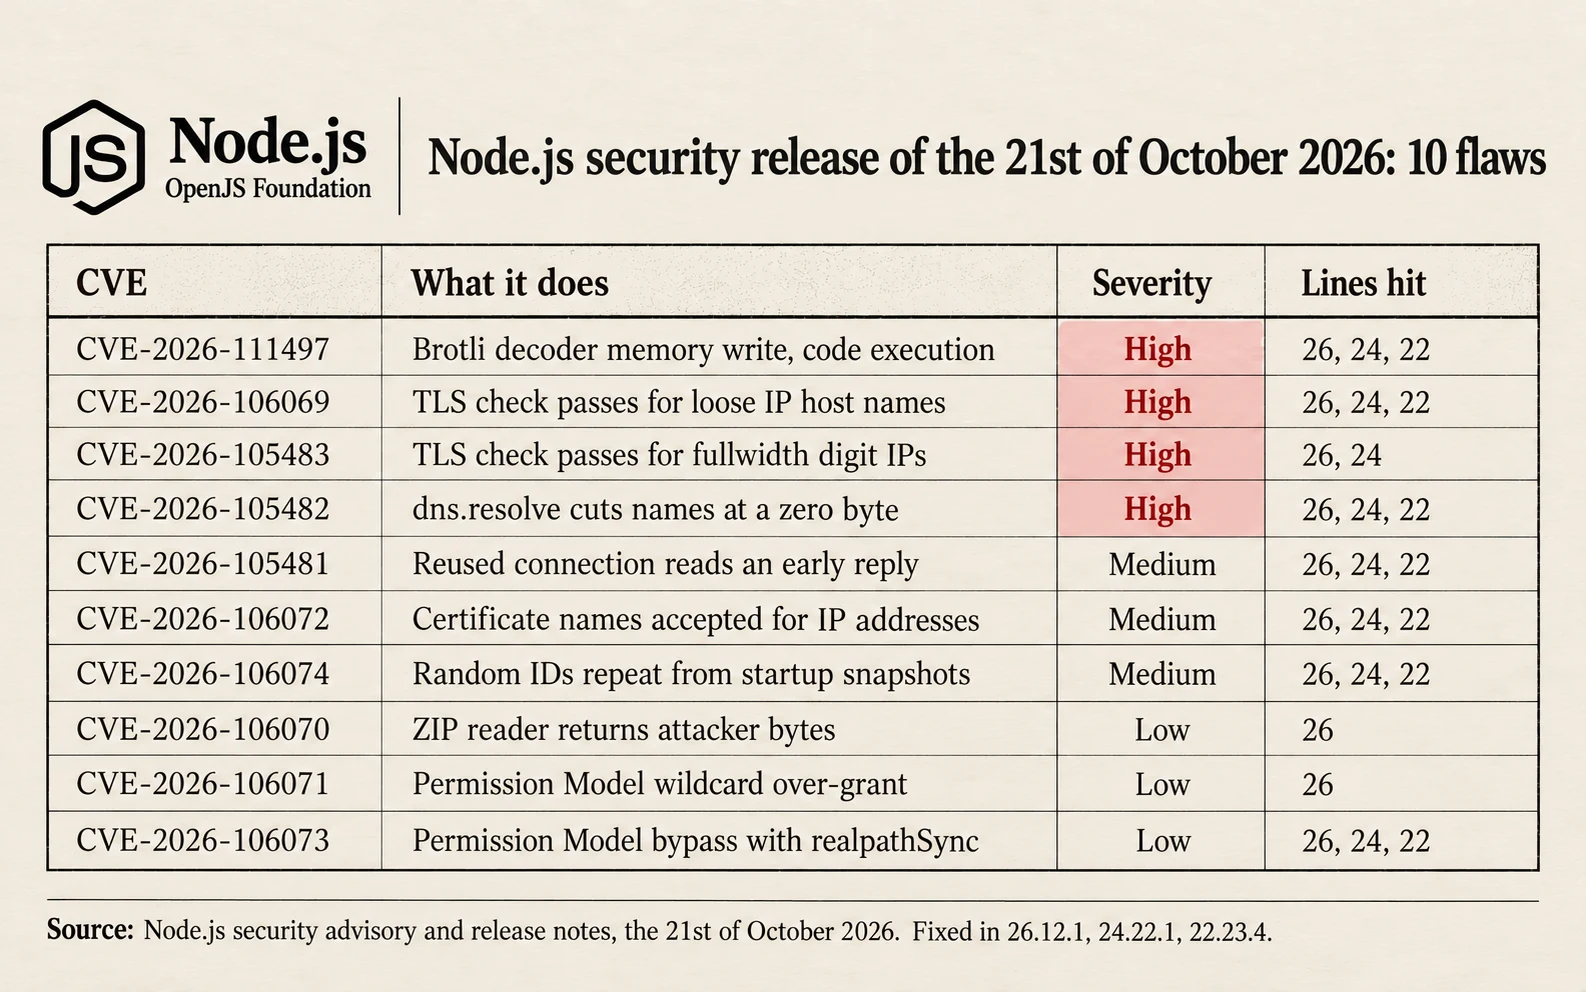
The Node.js project fixed 10 security flaws in its 26.x, 24.x and 22.x lines on the 21st of October 2026, its advisory says. Four of them are rated high.
The worst one, CVE-2026-111497, sits in the Brotli decoder, the code that unpacks compressed data. The project says it permits remote code execution, a way for an attacker to run their own commands on a server.
Update to Node.js 26.12.1, 24.22.1 or 22.23.4 now
The fixed versions are 26.12.1, 24.22.1 and 22.23.4, the project's release notes of the 21st of October say.
Node.js 20 and 25 get no fix. Their support ended on the 30th of April and the 1st of June 2026, the project's release schedule shows.
Below we break down the four high flaws: one code execution, two TLS bypasses, one DNS bug
A crafted Brotli stream can corrupt memory, leak data or crash the program, Google's CVE record of the 22nd of October says. OpenAI's Codex Security team reported it, the advisory says.
TLS is the lock behind https, and its certificate check proves a server is who it says. Two flaws let that check pass for the wrong server, the advisory says.
CVE-2026-106069 hits when a host name loosely resolves to an IP address. CVE-2026-105483 hits when the IP address is written in fullwidth digits, and affects only 26.x and 24.x.
CVE-2026-105482 is the DNS bug. Its dns.resolve function, which looks up names, cut them at a hidden zero character.
Three medium flaws and three low ones
One medium flaw lets a reused connection read a reply sent before the request. Another makes random IDs repeat across processes started from one snapshot.
Two low flaws slip past the Permission Model, a feature that limits which files code can touch. The update also drops trust in eMudhra's compromised certificates, the advisory says.
What is confirmed and what is not
Node.js rates the Brotli flaw high, while Google's CVE record scores it 9.2 out of 10, critical. Nine of the 10 CVE records were still missing from cve.org on the 23rd of October 2026.
The advisory and release notes name no attacks so far.
Key facts
Released by the Node.js project, the 21st of October 2026.
10 flaws: four high, three medium, three low.
Fixed in 26.12.1, 24.22.1 and 22.23.4.
Worst flaw: CVE-2026-111497 in Brotli, 9.2 out of 10.
Source: Node.js security advisory of the 21st of October 2026