Palo Alto VPN flaw: 2 ransomware gangs inside
Palo Alto Networks' Unit 42 wrote on the 19th of October 2026 that the Qilin and INC ransomware groups enter networks through CVE-2026-0257 in GlobalProtect VPN. Fixes have existed since the 13th of May.
 Palo Alto's PAN-OS GlobalProtect flaw
Two ransomware groups get in through a fixed flaw in Palo Alto Networks' firewalls, its Unit 42 team wrote on the 19th of October 2026. Ransomware locks a victim's files until they pay.
Unit 42 named Spikey Scorpius, also called Qilin, and Tarnished Scorpius, also called INC. The flaw, CVE-2026-0257, scores 7.8 out of 10, Palo Alto's advisory says.
The flaw opens a VPN session without a password or phone code
The bug sits in GlobalProtect, the VPN in Palo Alto's PAN-OS firewalls and its Prisma Access cloud, the advisory says. A VPN is a private tunnel into a company network.
Attackers skip both the password and the phone code step, Unit 42 wrote. Only firewalls with "authentication override" cookies turned on are at risk, the advisory says.
In one case attackers reached vCenter and a domain controller's disk
In one case attackers reached vCenter, which runs a company's virtual machines, Unit 42 wrote on the 20th of October.
They turned off security settings on VMware ESXi servers and copied logins from a domain controller's virtual disk. That way the guard software inside the machine never sees it, the brief says.
Below we break down who is affected, the fixed versions and what to do
Palo Alto published its advisory on the 13th of May 2026. Its Cloud NGFW and Panorama are safe, the advisory says.
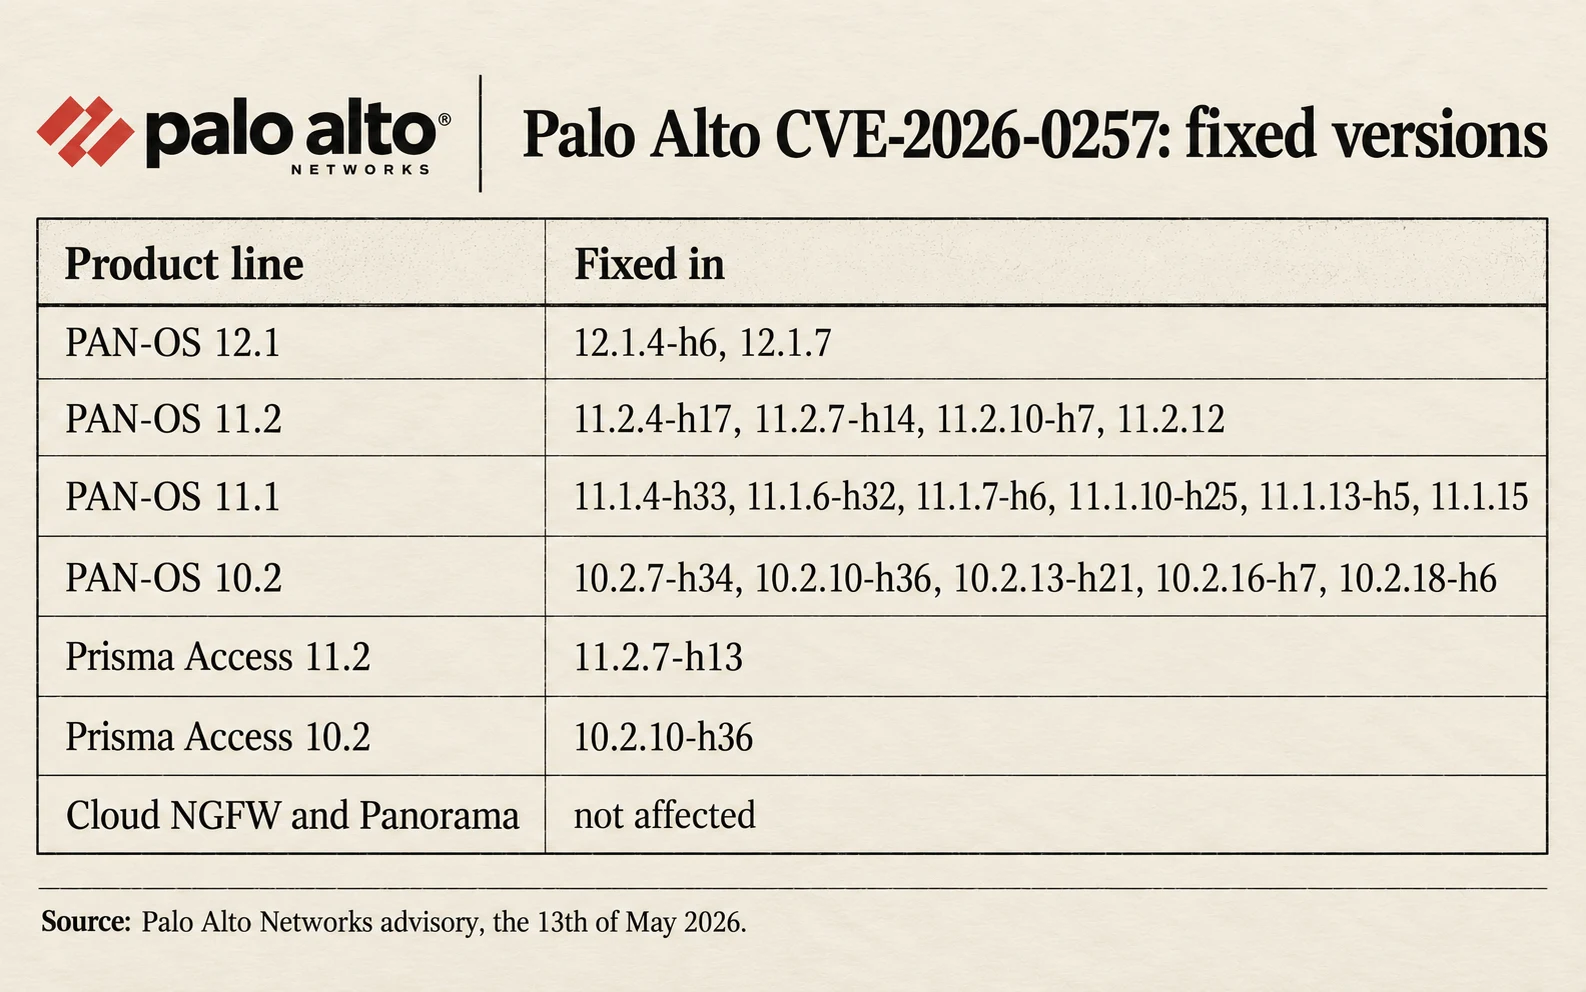
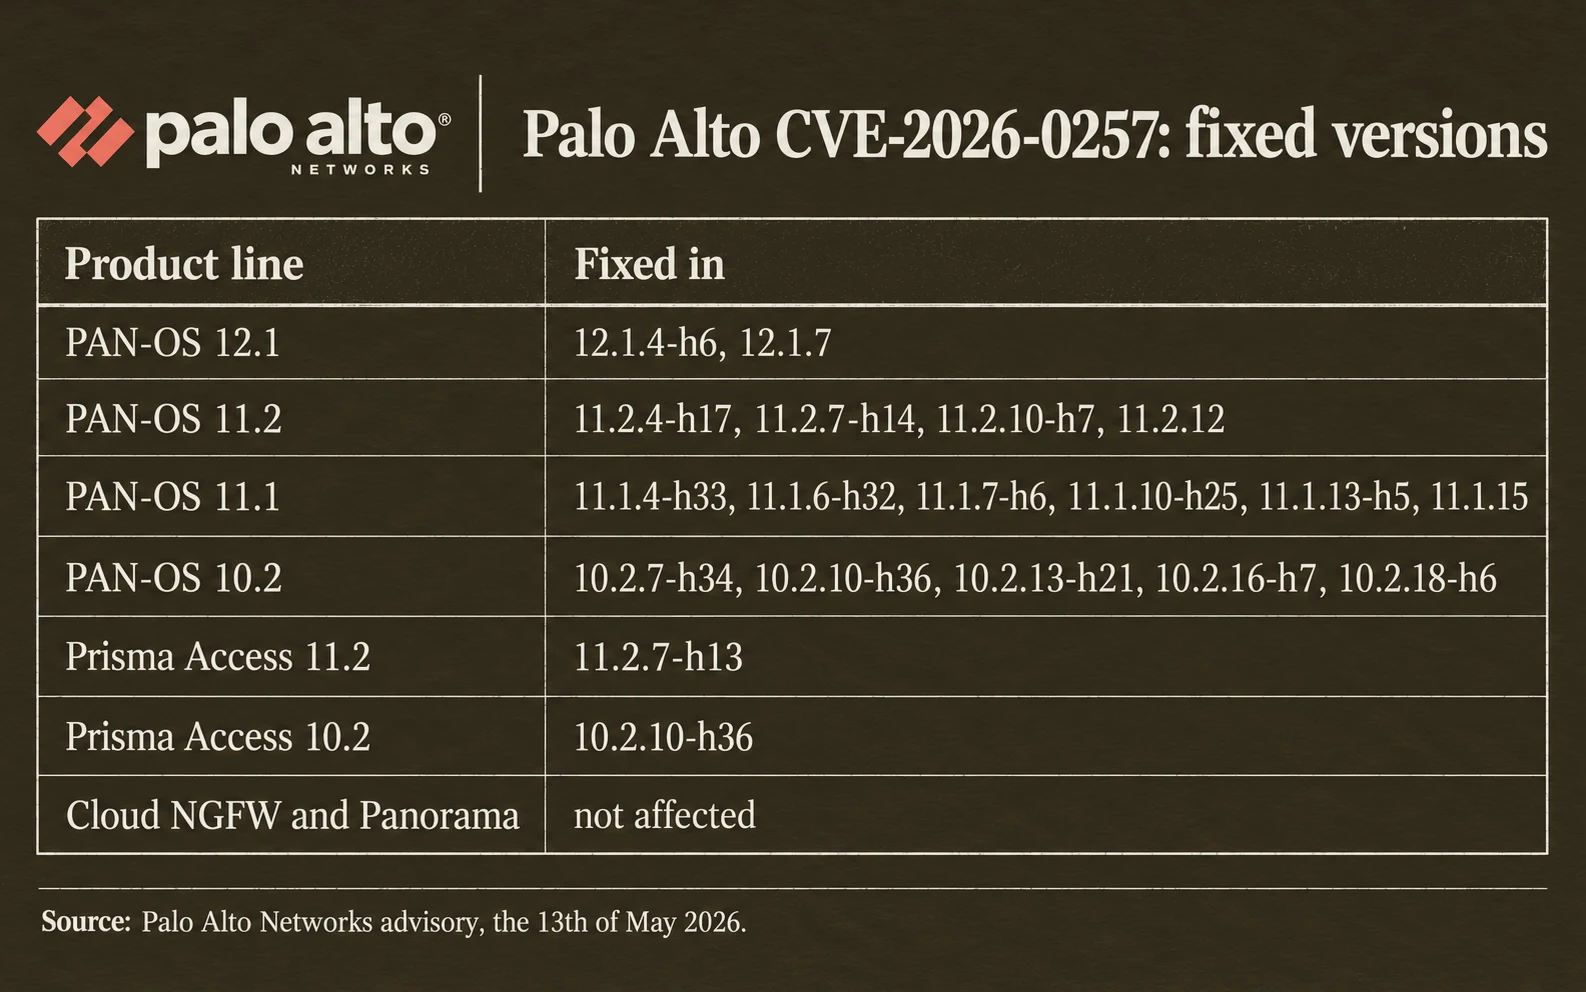
Admins who cannot upgrade can switch the override cookies off, or give them their own certificate, the advisory says.
Unit 42 asks admins to search VPN logs for its listed addresses and treat any match as a possible break-in.
What is confirmed and what is not
CISA, the US cyber agency, lists the bug as exploited from the 29th of May 2026, its data feed shows. Unit 42 says the 13th of May.
ReliaQuest also tied a group called Settra to the flaw, The Hacker News reported on the 20th of October. Unit 42 has not confirmed that link.
Key facts
Palo Alto's CVE-2026-0257 scores 7.8 out of 10, fixed on the 13th of May 2026.
Qilin and INC ransomware use it, Unit 42 wrote on the 19th of October.
Unit 42 gave no count of victims.
Source: Palo Alto Networks Unit 42 threat brief and security advisory