PHP2Shell: 32 UK state services go offline
Amazon saw a PHP2Shell exploit attempt on the 17th of October 2026, four days before PHP's fix of the 21st. The NSA and CERT-EU said servers that cannot be updated should go offline, and 32 UK government services did.
 The PHP project's PHP2Shell: sites go dark
An attacker tried the PHP2Shell flaws on the 17th of October 2026, four days before PHP's fix, Amazon wrote on the 21st. Attacks now run into the millions, and governments have switched websites off.
PHP2Shell is two flaws in PHP, CVE-2026-109618 and CVE-2026-109619. They allow remote code execution, a way for an attacker to run commands on a web server.
Amazon saw the first attempt on the 17th, Cloudflare now counts millions
Amazon's decoy servers caught the attempt from a service that hides the sender's address, security chief CJ Moses wrote. "It remains unclear how the actor acquired exploit information prior to disclosure," he wrote.
Cloudflare saw tens of thousands of attempts within 45 minutes of disclosure, chief executive Matthew Prince said, The Register reported on the 22nd. The count has since reached the millions, The Register wrote.
Below we break down who warned and who went offline
CERT-EU, the EU institutions' cyber team, told groups on the 21st to patch at once, Reuters reported. Those unable to patch should consider taking sites offline, CERT-EU said.
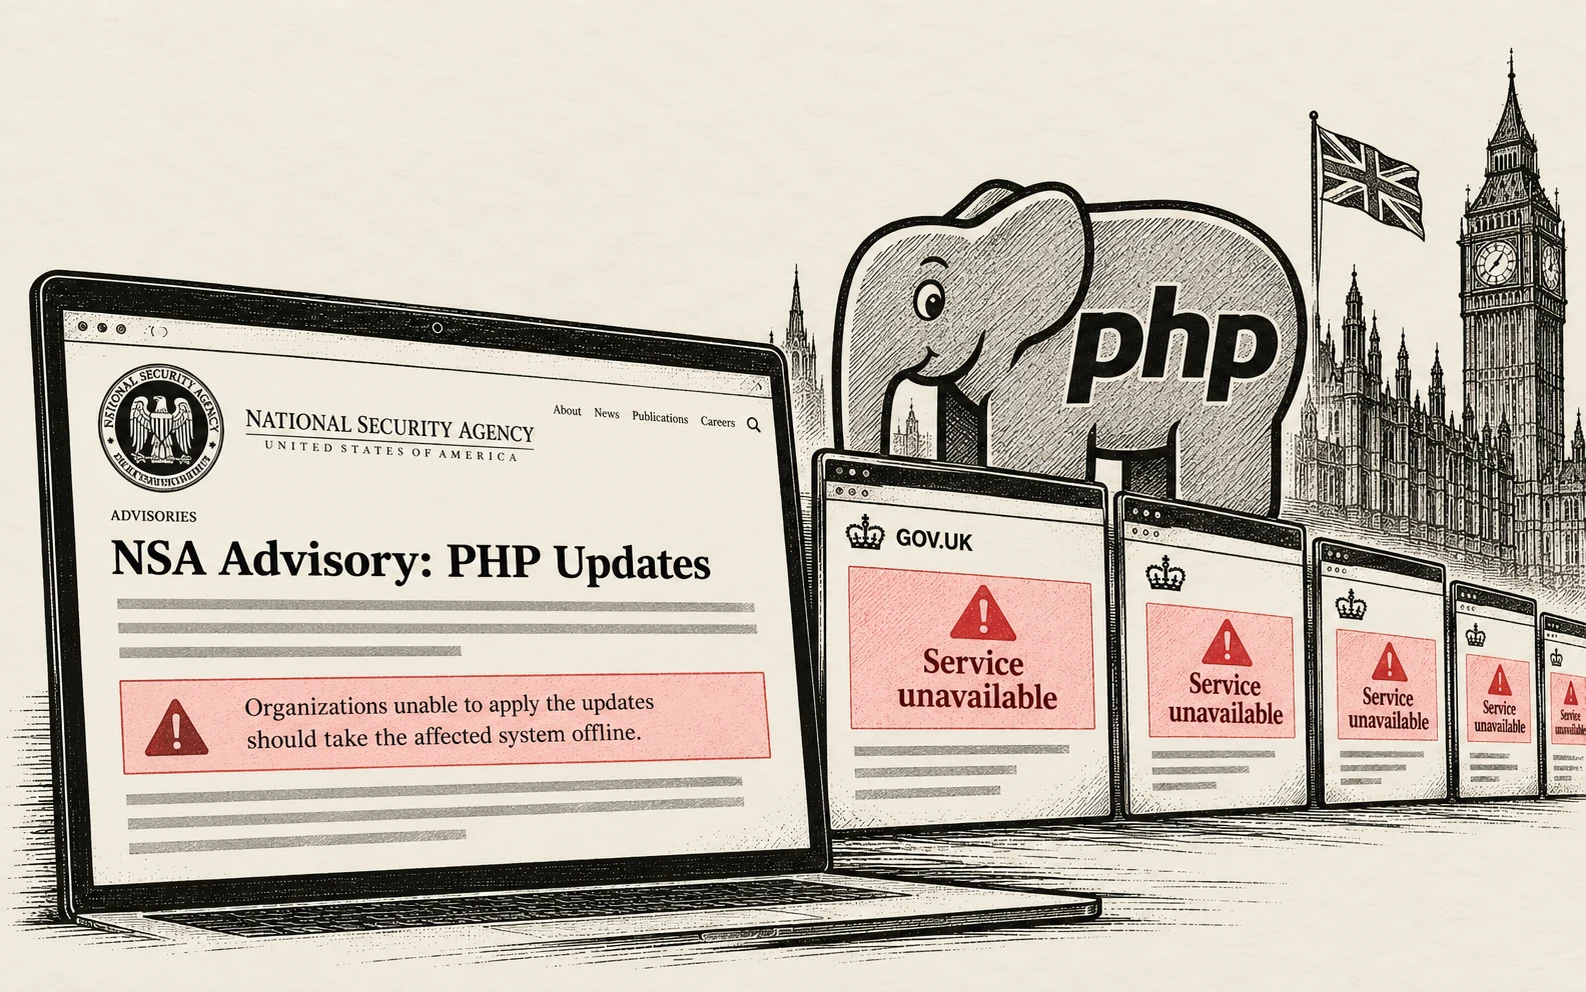
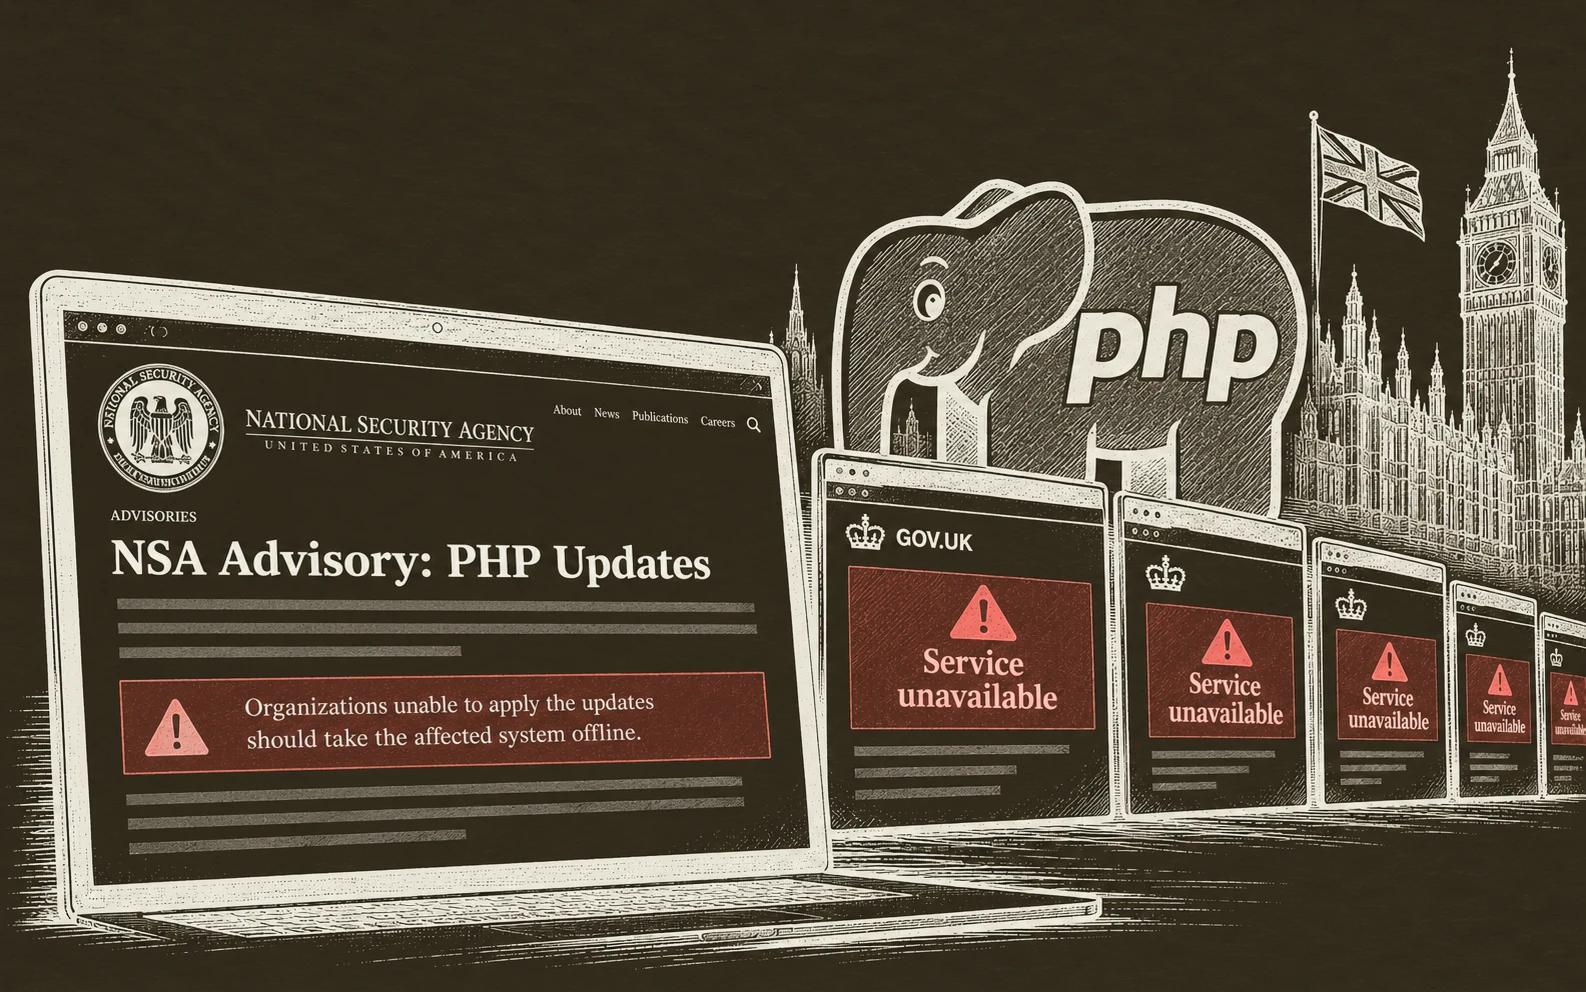
The NSA advised on the 21st that a system that cannot be updated at once should go offline, its press release says.
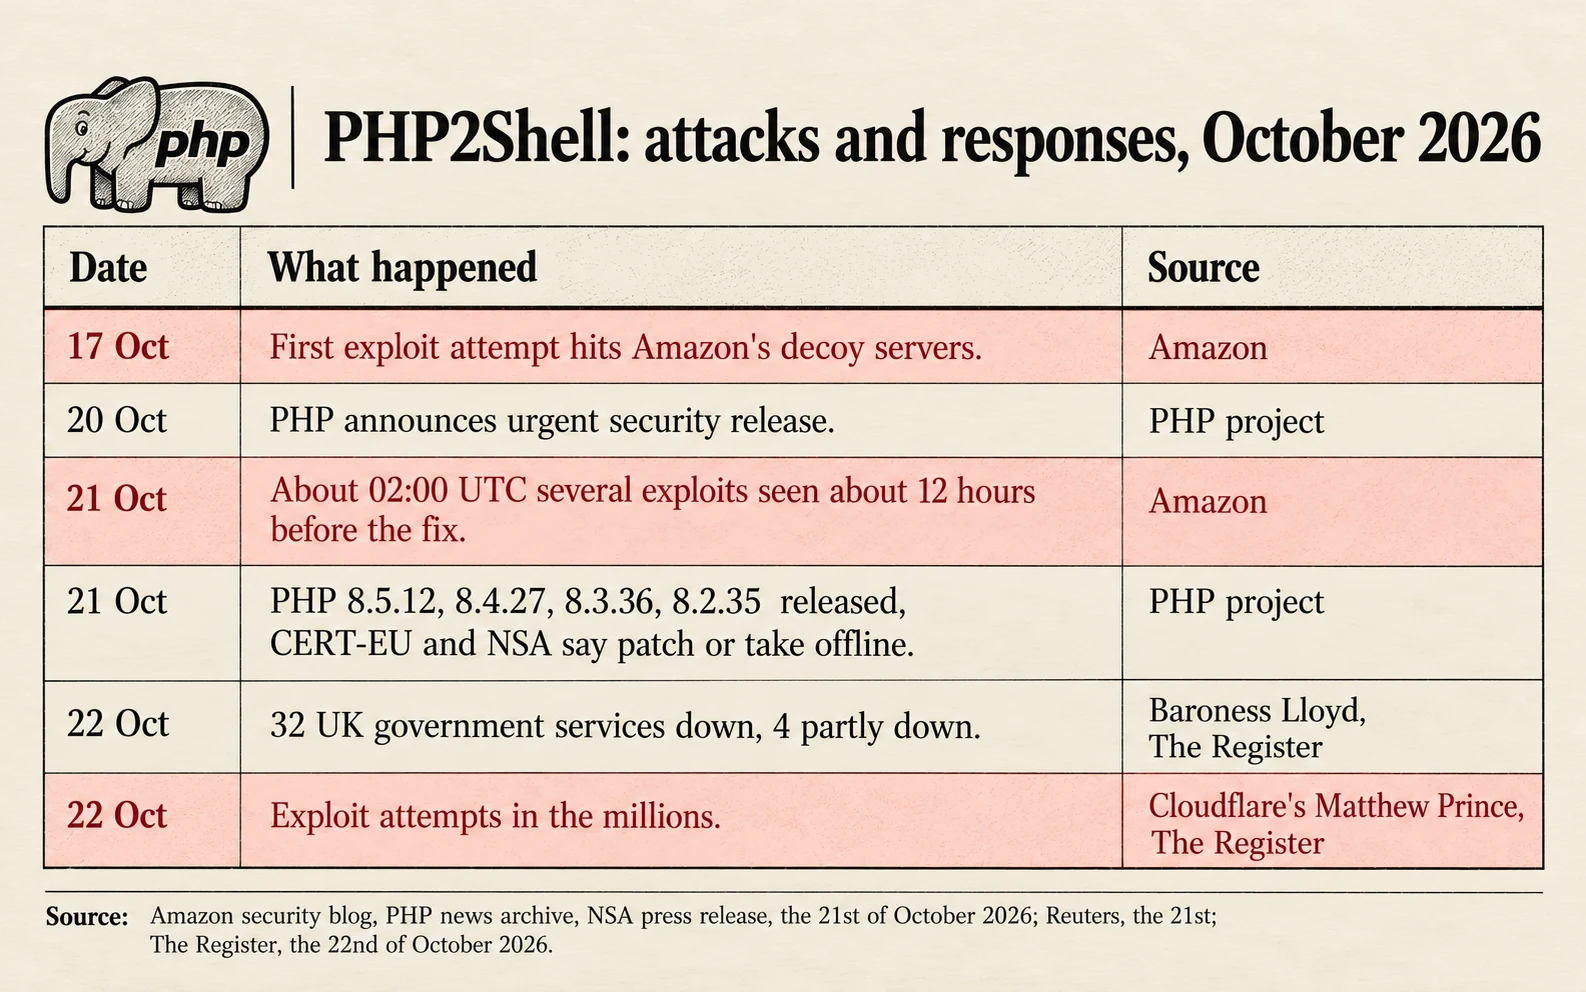
On the 22nd, 32 UK government services were down and 4 partly down, minister Baroness Lloyd told Parliament, The Register reported. She knew of no break-in.
The Dutch state login site DigiD was closed for most of the 21st, the news agency ANP reported.
What to do now: update to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35
"There are no complete mitigations, updating is the only safe choice," the PHP project wrote on the 21st. PHP 8.1 and older need a fix from a vendor or an upgrade.
Amazon advised checking server logs from the 17th of October onward.
What is confirmed and what is not
The US agency CISA had seen no attacks when it wrote its advisory, ITPro reported. CISA's list of exploited flaws, version 2026.10.21, carries neither CVE.
No agency has named a group behind the attacks as of the 23rd. Amazon wrote that varied payloads suggest several attackers.
Key facts
First exploit attempt on the 17th of October 2026, Amazon wrote.
PHP fixed both flaws on the 21st of October 2026.
Attempts in the millions, Cloudflare's chief said.
32 UK government services offline on the 22nd.