PingCAP's TiDB Cloud breached for 28 days
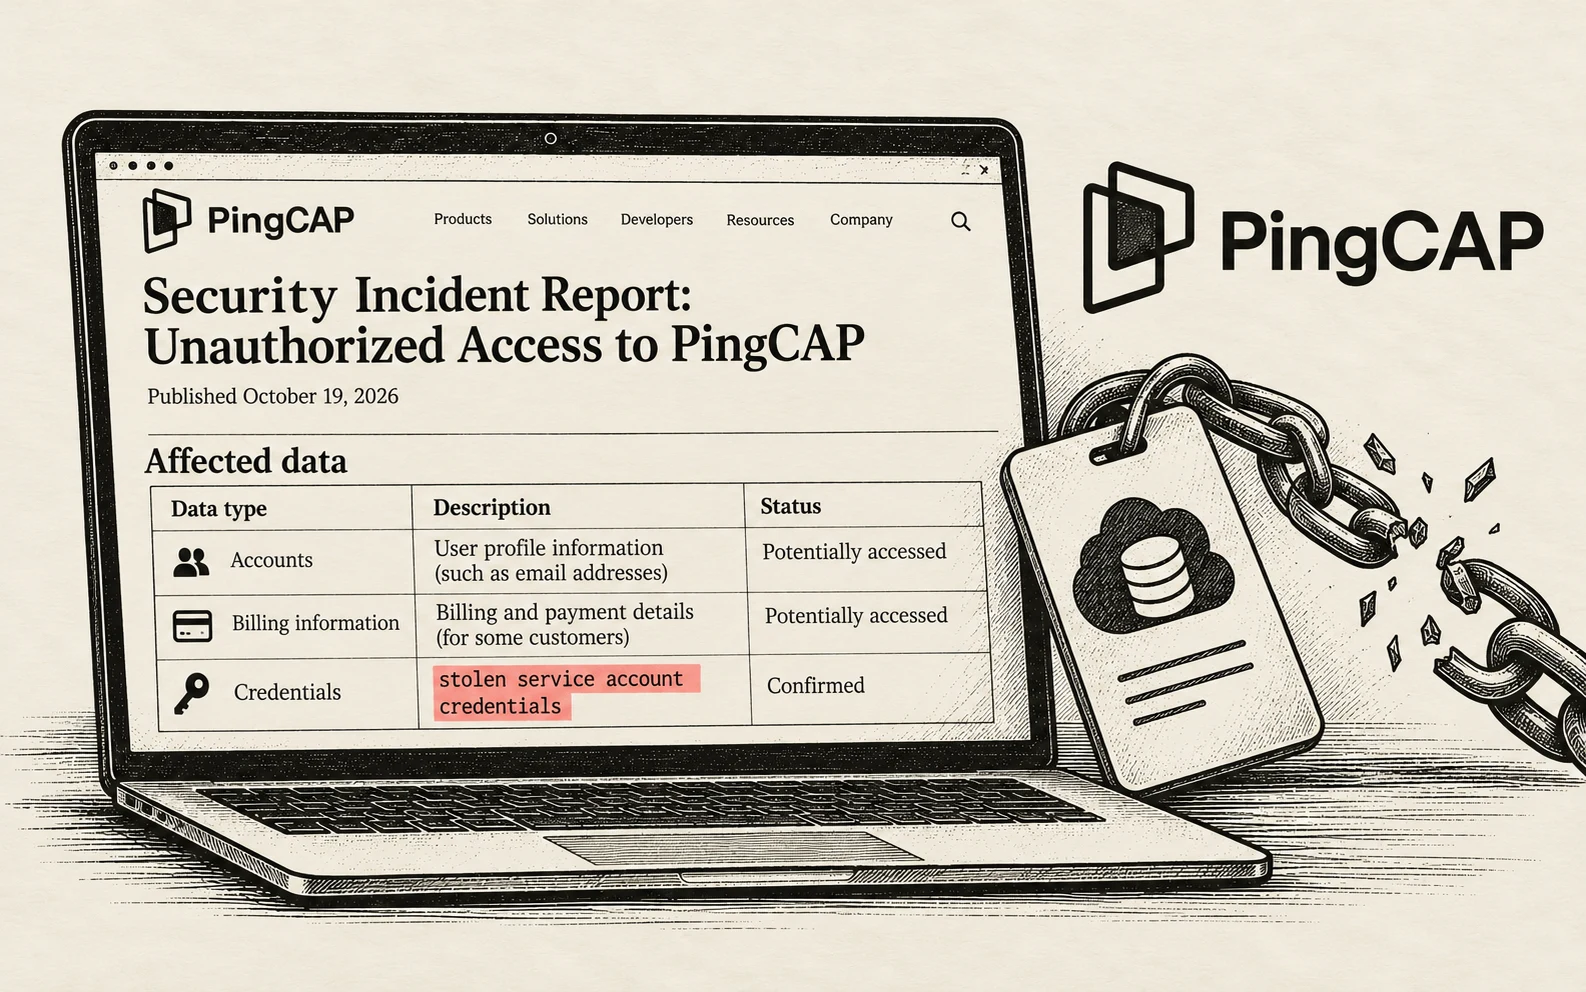
PingCAP said on the 19th of October 2026 that an attacker with stolen credentials copied TiDB Cloud account, SQL editor and billing records. Customers are asked to rotate API keys.
 PingCAP's TiDB Cloud, 28 days breached
PingCAP said on the 19th of October 2026 that an attacker was inside its internal systems for 28 days. The intruder used stolen service account logins from the 9th of September to the 7th of October, its incident report says.
A service account is a login used by software. The attacker copied data and source code, PingCAP wrote, but it found "no evidence that data stored in TiDB was impacted."
TiDB Cloud user names, emails, SQL editor text and billing records were copied
Copied records held user names, email addresses and text typed into the SQL editor, the report says. That is the box where users type database commands.
Customer contacts, contract terms, pricing and billing settings were also copied, PingCAP wrote. Not every customer lost every kind of data.
Up to about 50,000 personal records in Japan, no global count
PingCAP's Japanese page said on the 21st of October 2026 that up to about 50,000 personal records in Japan leaked. The English report gives no total.
Below we break down the timeline, from the 9th of September to the 21st of October
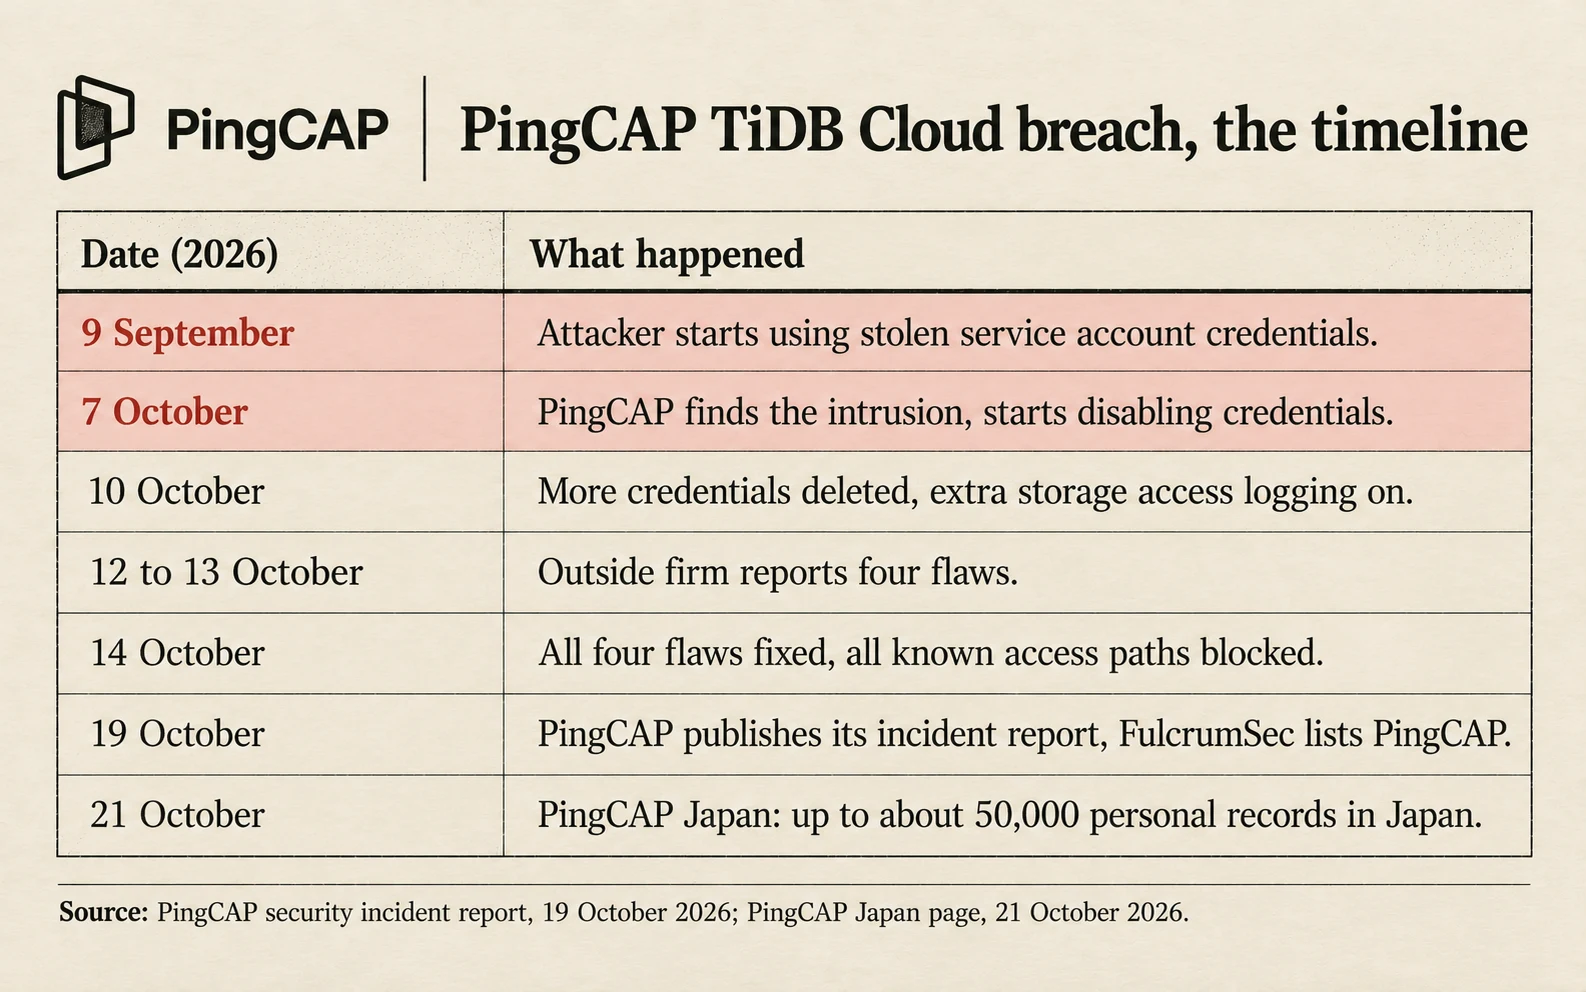
An outside firm reported four flaws on the 12th and 13th of October, the report says. PingCAP fixed all four by the 14th and blocked every path it had found.
The report came out 12 days after PingCAP found the attack, by our arithmetic.
TiDB Cloud customers are asked to change API keys and check access logs
PingCAP's Japanese page asks customers to replace their TiDB Cloud API keys, the secret codes programs use to run an account. It also asks them to check access logs and remove unused accounts.
PingCAP never asks for passwords or keys by email, the page says. The English report lists no customer steps, as of the 23rd of October 2026.
What is confirmed and what is not
The English report says a copied table held locked API key values. The Japanese page says only the public half of each key leaked.
A group called FulcrumSec claims it took 10.6 terabytes in 4.9 million files, Crypto Briefing reported on the 20th of October. PingCAP says the attacker's claims about logins have not been checked.
Key facts
Attacker inside for 28 days, until the 7th of October 2026.
User names, emails, SQL editor text and billing records copied.
Up to about 50,000 personal records leaked in Japan.
Replace TiDB Cloud API keys and watch for fake PingCAP emails.
Source: PingCAP security incident report