Plex2Shell: 4 Plex flaws now exploited
Plex wrote on the 19th of October 2026 that four chained flaws in its Plex Media Server are under wide attack. Builds before 1.43.3.10861 are open, and Censys counted about 97,000 such servers by our arithmetic.
 Plex's Media Server, under attack
Attackers are breaking into Plex Media Server through four chained flaws called Plex2Shell, Plex wrote on the 19th of October 2026. The flaws are "being actively and widely exploited," the company wrote.
Plex Media Server is software people run at home to stream their own films. Every build before 1.43.3.10861 is open to the attack, Plex wrote.
Hacked Plex servers run crypto miners and proxy software
Hacked servers ran cryptocurrency miners, which use the computer to earn money for the attacker, Plex wrote. They also ran proxy software that sends strangers' traffic through the owner's connection.
Below we break down the four flaws, the dates and the 97,000 open servers
Plex's update lists four CVEs, the public ID numbers for flaws. CVE-2026-96652 makes the server send web requests for anyone, with no password.
CVE-2026-96654 reaches internal functions, and CVE-2026-96655 leaks the owner's admin key. CVE-2026-96656 writes a file into the Codecs folder, which the server then runs.
Chained, they let a stranger run their own commands on the server, Plex wrote.
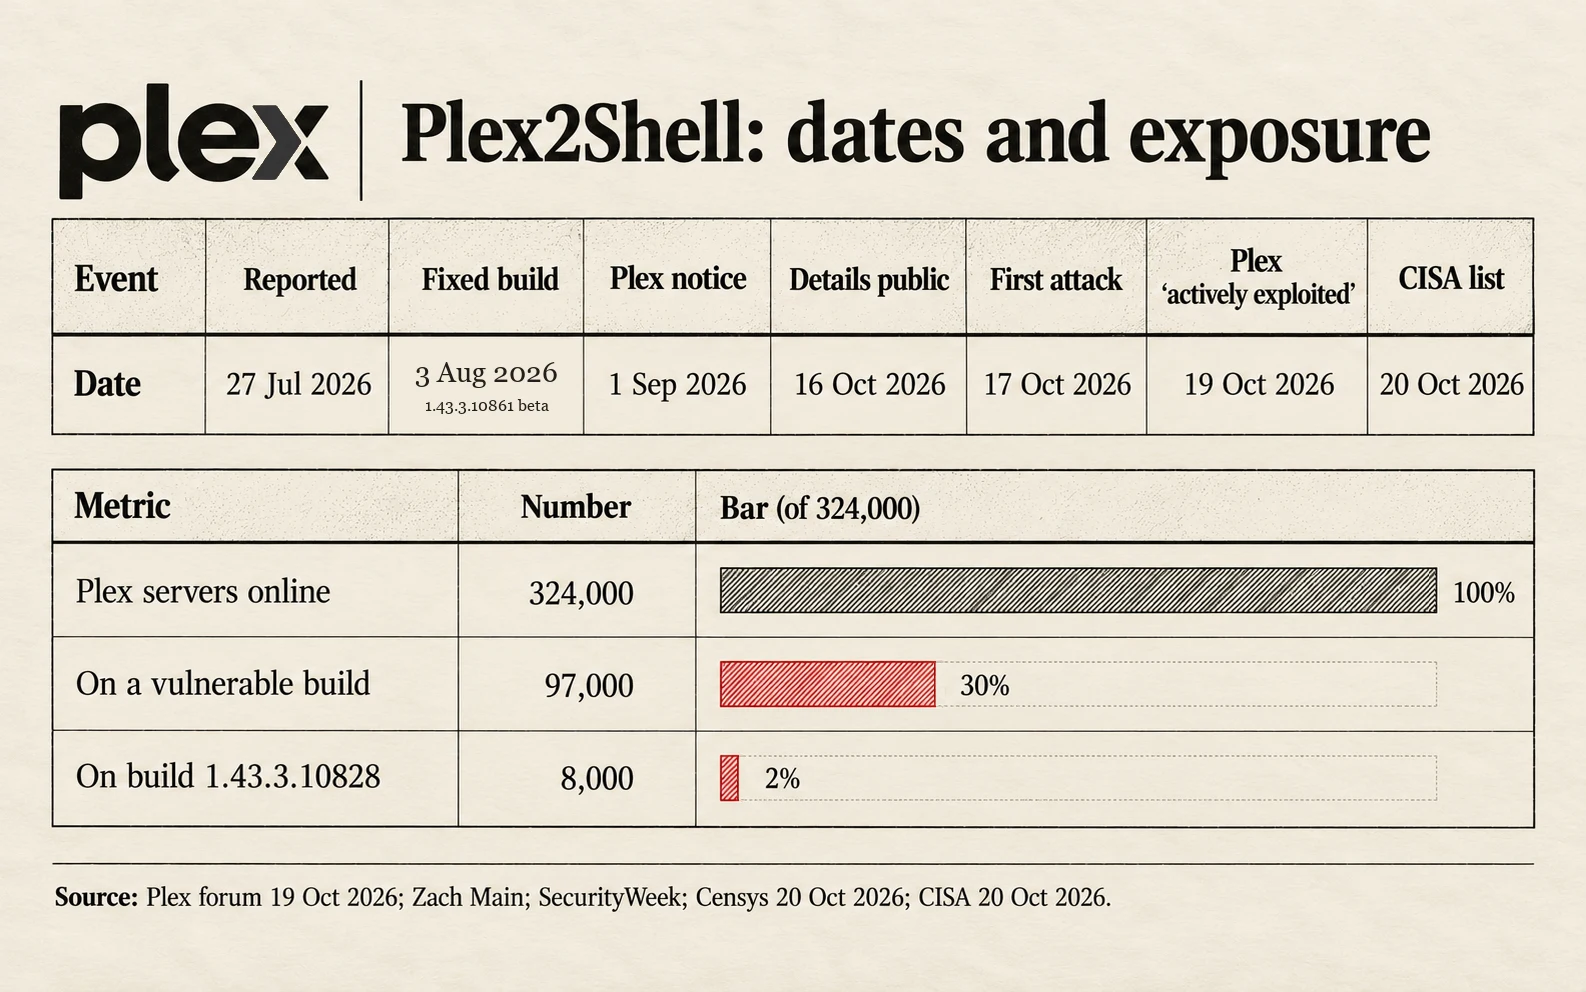
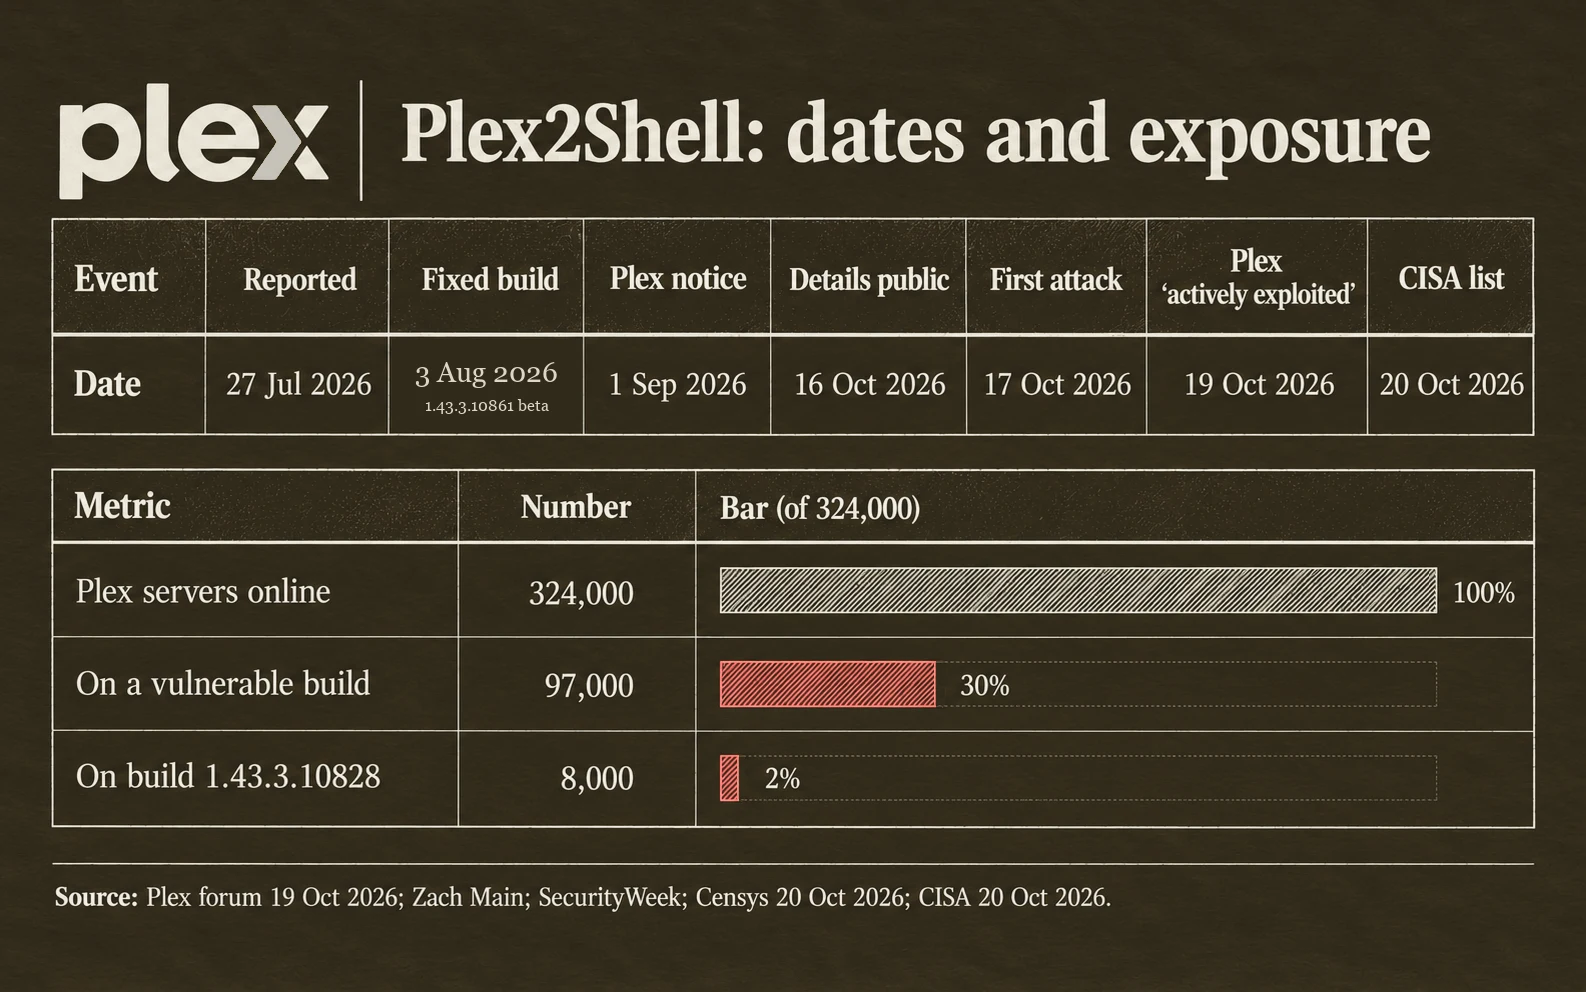
Researcher Zach Main reported the flaws on the 27th of July 2026, his blog says. He published the details on the 16th of October, and a trap server saw the first attack the next day, SecurityWeek reported.
Censys, an internet scanning firm, counted about 324,000 Plex servers online on the 20th of October. About 30 percent ran a vulnerable build, roughly 97,000 by our arithmetic.
How to check a Plex server and what to do now
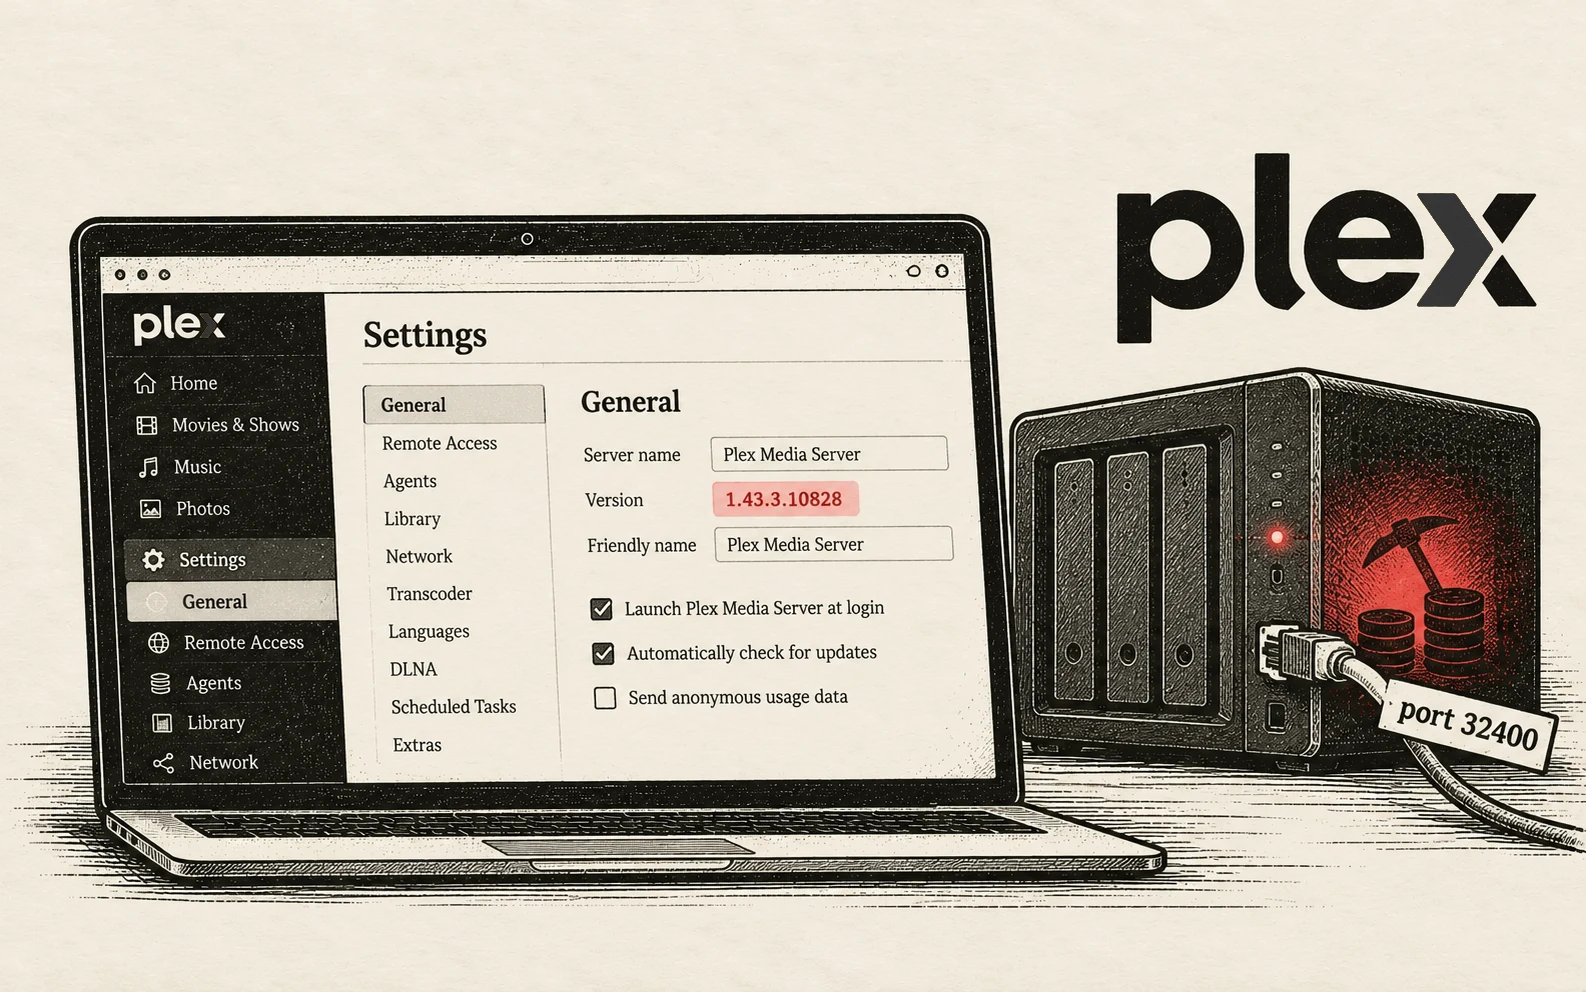
Plex Web shows the version under Settings, then General. An older server reachable from the internet may already be hacked, Plex wrote.
Signs are unknown programs, strange files in the Codecs folder and a busy processor with nothing playing. Plex advises a clean reinstall when in doubt, then signing out all devices and a new password.
Plex also advises turning off Remote Access when unused and closing port 32400, the server's network door.
What is confirmed and what is not
The Hacker News describes two of the flaws differently from Plex, and this story follows Plex. The US agency CISA listed all four as exploited on the 20th of October 2026.
Key facts
Plex2Shell attacks began on the 17th of October 2026.
Fixed in build 1.43.3.10861 and later.
About 97,000 servers still open, by our arithmetic.
Close port 32400 if Remote Access is unused.
Source: Plex's security update on the Plex forum, updated the 19th of October 2026