Railway breach: AI keys of 100,000 at risk
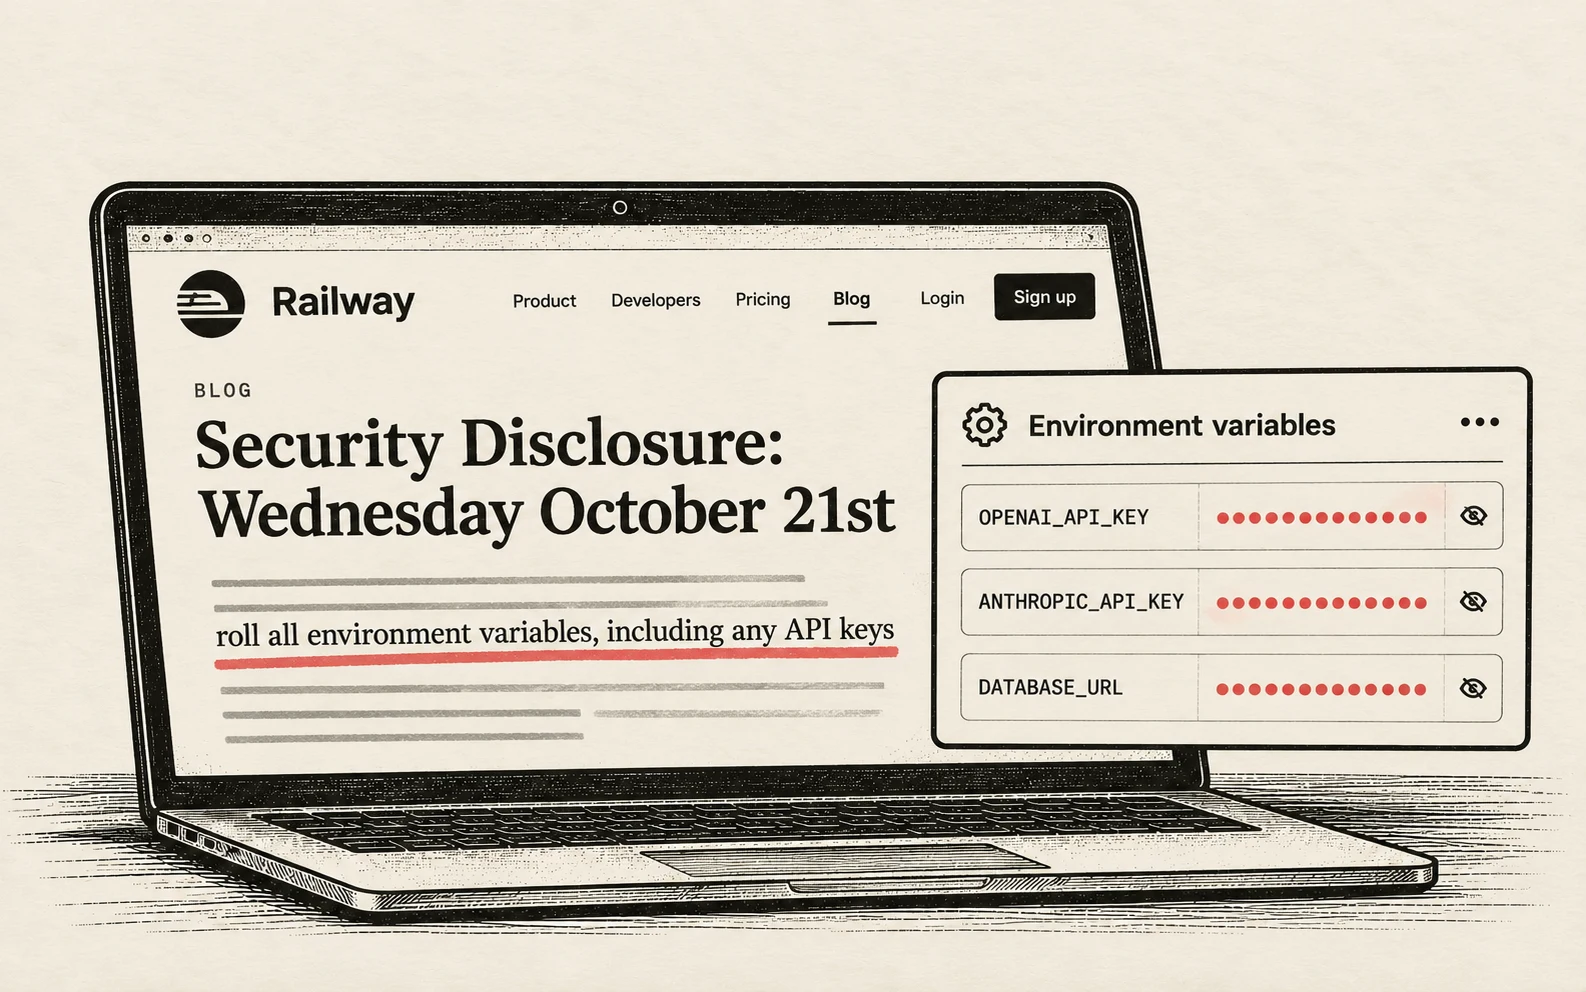
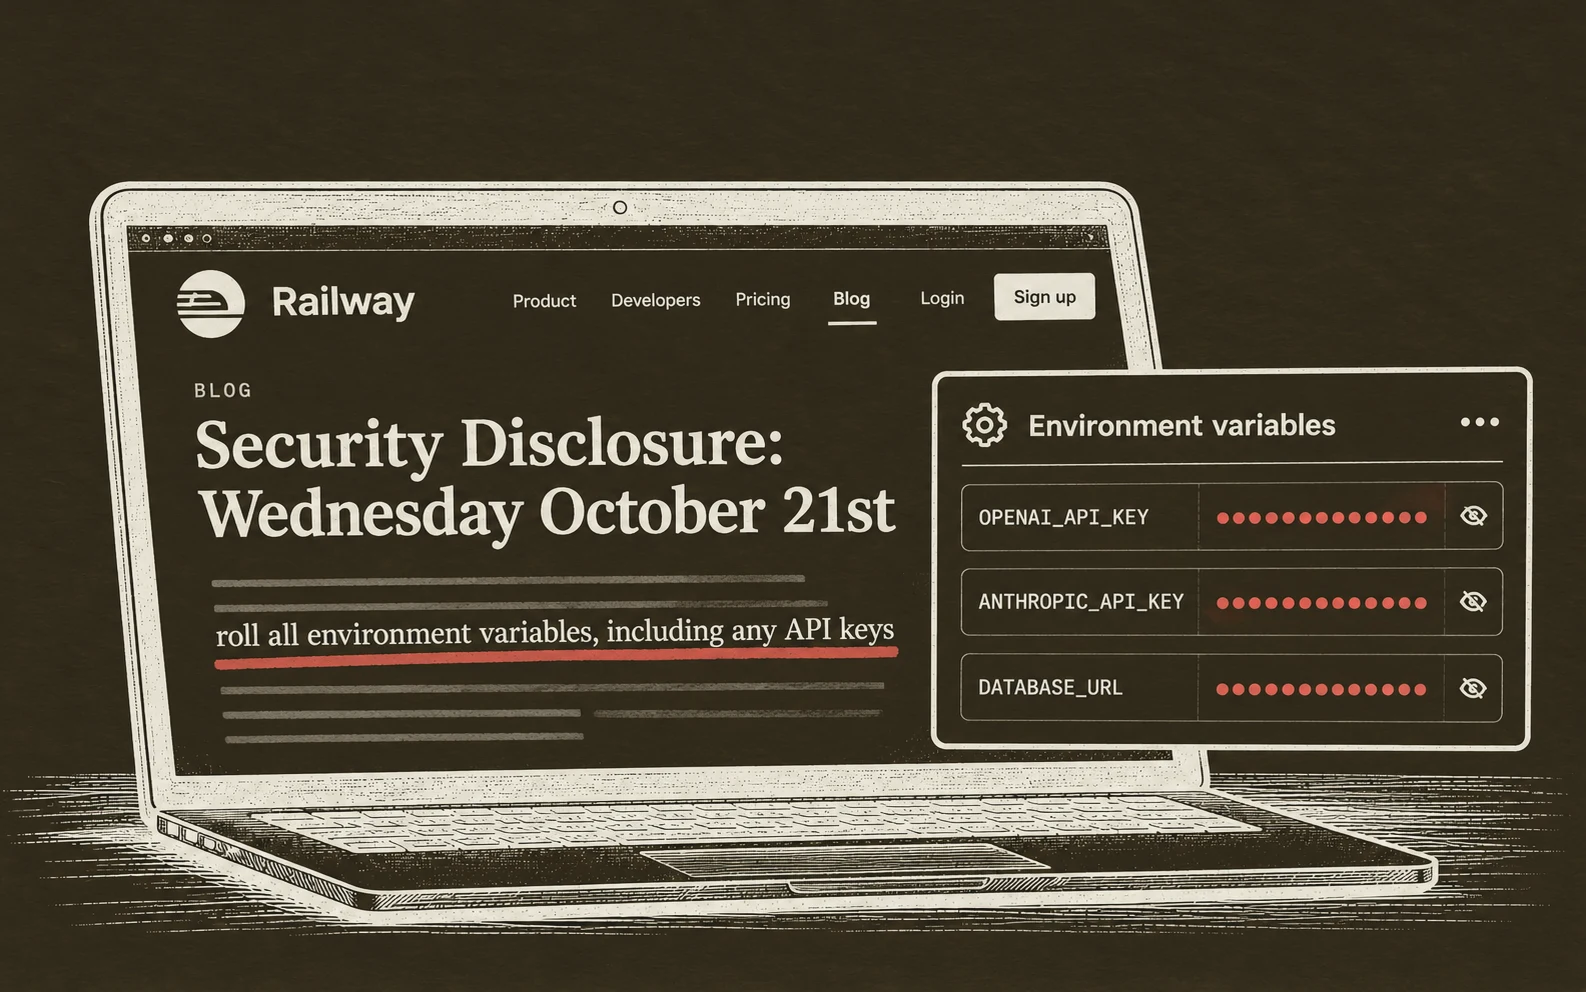
Railway said on the 21st of October 2026 that an attacker may have read its customers' secret keys. Its first report puts the number at up to 100,000 workspaces, and it asks every user to change their keys.
 Railway: change your keys now
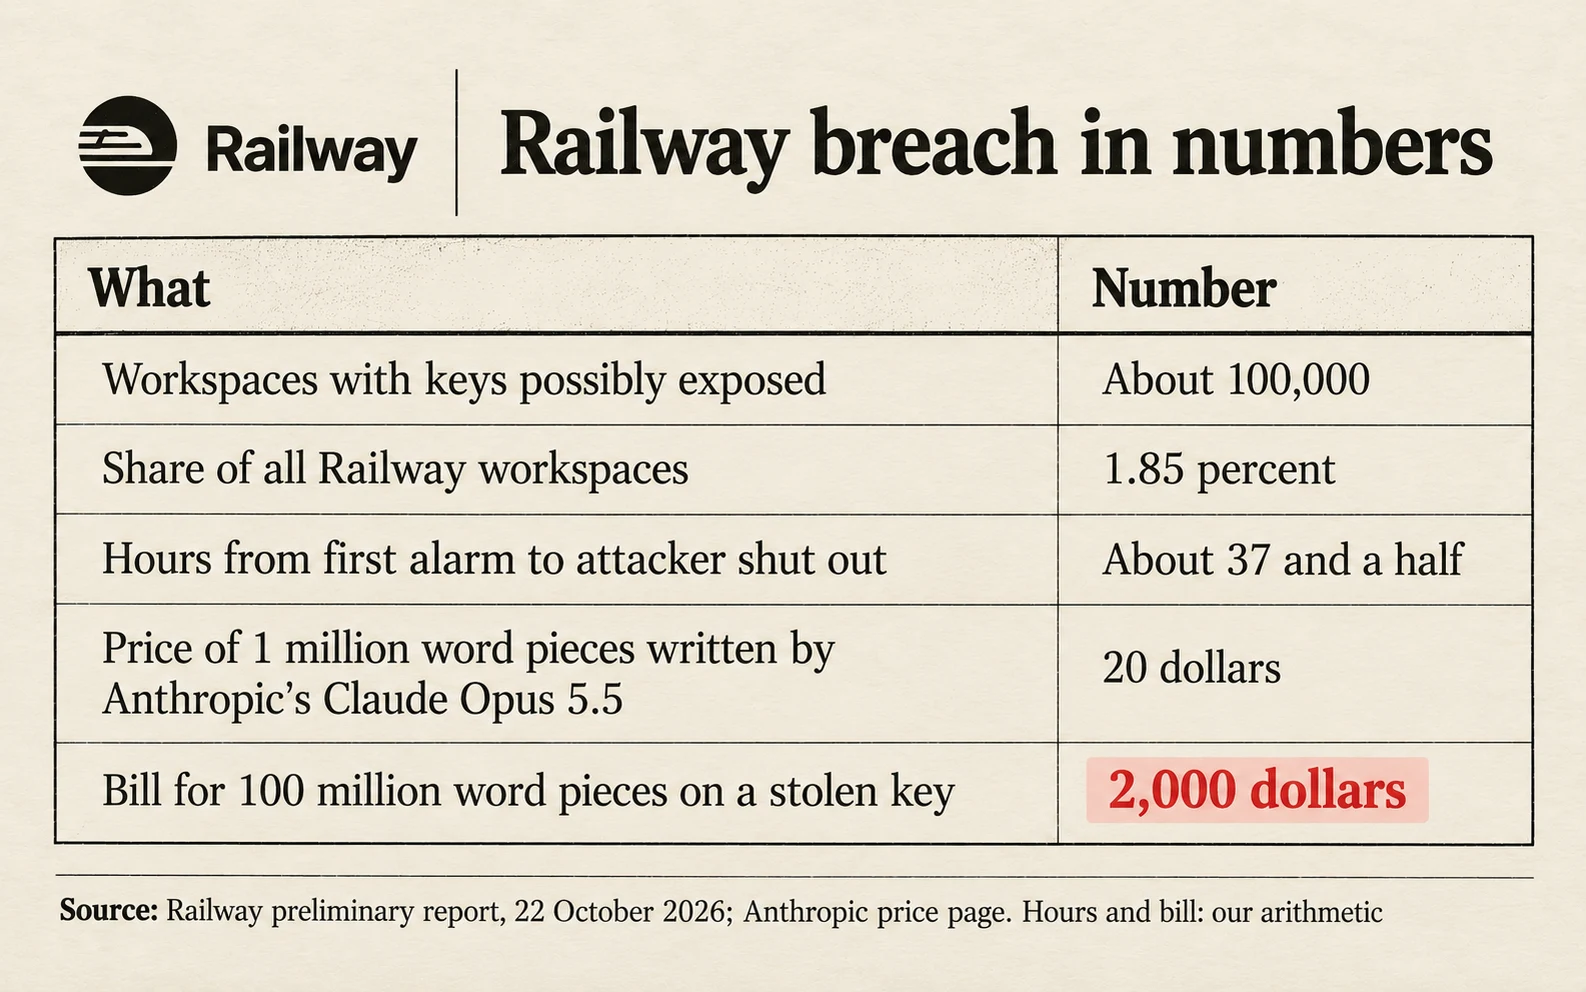
Railway, a company that runs other businesses' apps, said on the 21st of October 2026 that an attacker may have read customers' secret keys. Its first report says up to 100,000 workspaces may have had keys exposed.
That is about 1.85% of all its workspaces, Railway wrote. A workspace is one customer's space on Railway, and the attacker was hunting for keys to AI services.
What environment variables and API keys are
An app keeps its settings in environment variables, small notes stored next to its code. Many of those notes hold API keys.
An API key works like a password that lets one program use another company's paid service. Whoever holds the key can use it, and the owner pays.
Below we break down what happened, by Railway's own timeline
Railway's alarms went off on the 20th of October, its report says. The attacker copied keys in locked form, then found more passwords and unlocked part of them on the 21st.
Railway said the attacker was shut out on the 22nd, about 37 hours after the first alarm. Running apps stayed online, but new app updates were paused.
Why a stolen AI key costs its owner money
AI services charge by the token, a small piece of a word. Anthropic's price page lists 20 dollars for every million tokens its Claude Opus 5.5 model writes.
If a thief made that model write 100 million tokens, the key's owner would owe 2,000 dollars, by our arithmetic. Railway wrote that the attacker wanted keys to copy AI models by asking them huge numbers of questions.
Railway asked Anthropic, OpenAI and others to cancel keys
On the 21st, Railway asked GitHub, Anthropic, OpenAI, Stripe and others to cancel keys at risk, its report says. It emailed the customers at highest risk by the 23rd of October.
What Railway tells customers to do
Anyone who signed up before the 21st of October should make new keys and cancel the old ones, Railway said.
What is confirmed and what is not
Railway has not named the attacker. Its website says over 2 million developers use it, while BleepingComputer reported 4.8 million users on the 22nd of October.
Key facts
Railway disclosed the attack on the 21st of October 2026.
Up to 100,000 workspaces had keys exposed, about 1.85%.
The attacker wanted keys to AI services.
Railway asks every user to make new keys.
Source: Railway, Preliminary Report: Oct 21st Security Incident